Choosing a security or compliance product requires more than reading feature lists and listening to polished demos. Two vendors may both claim “risk management,” “reporting,” and “evidence capture,” but deliver very different outcomes when you need to reconstruct an incident or hand evidence to an auditor.
This guide gives CISOs, IT managers and compliance owners a repeatable method: start from the outcome you need, insist on eliminatory requirements before demos, run the same hands-on scenario with every candidate, and score results based on verifiable evidence — not promises.
Start by defining the exact problem you want to solve
The very first decision is to identify the category of product you need. For example:
- Endpoint protection platforms act on threats and block or remediate malware.
- Monitoring and SIEM platforms collect, correlate and alert on telemetry.
- Compliance and audit platforms organize controls, owners and evidentiary records.
These categories often complement one another but are not interchangeable. State the expected operational result in concrete terms: “detect and report unprotected endpoints,” “reconstruct privileged access in the last 90 days,” or “demonstrate execution of quarterly controls.” Avoid vague goals like “be compliant.”
Also define what remains outside the product’s scope. For instance, software can document the maintenance of a physical access control system, but it cannot replace the physical repair work. Make those boundaries explicit so vendors and evaluators don’t assume responsibility where none exists.
If your focus is managing checks, findings and follow-ups, refer to guidance about selecting audit-focused tools (see /en/blog/software-audit-interno) to make sure you’re comparing the right category.
Set eliminatory requirements before scheduling demos
Some requirements are deal-breakers and should not be traded for a lower price or a nicer UI. Create a short request specification that vendors must answer before you spend time on hands-on evaluations.
A practical specification covers four areas:
- Scope: systems, processes, sites and data types included, plus explicit exclusions.
- Responsibilities: who administers the product, who performs controls and who approves results.
- Constraints: authentication, integration, availability and export requirements.
- Acceptance: the tests, expected outcomes and conditions that disqualify a vendor.
Examples of eliminatory requirements:
- Ability to restrict access to authorized users only.
- Capability to export audit data in a usable form without an active subscription.
Classify everything as must-have, desirable or manageable by internal procedures. Assign verification owners: IT for integrations, Security for access controls, Compliance for evidence quality, Procurement for commercial terms.
Build a comparison grid that links requirements to observable tests
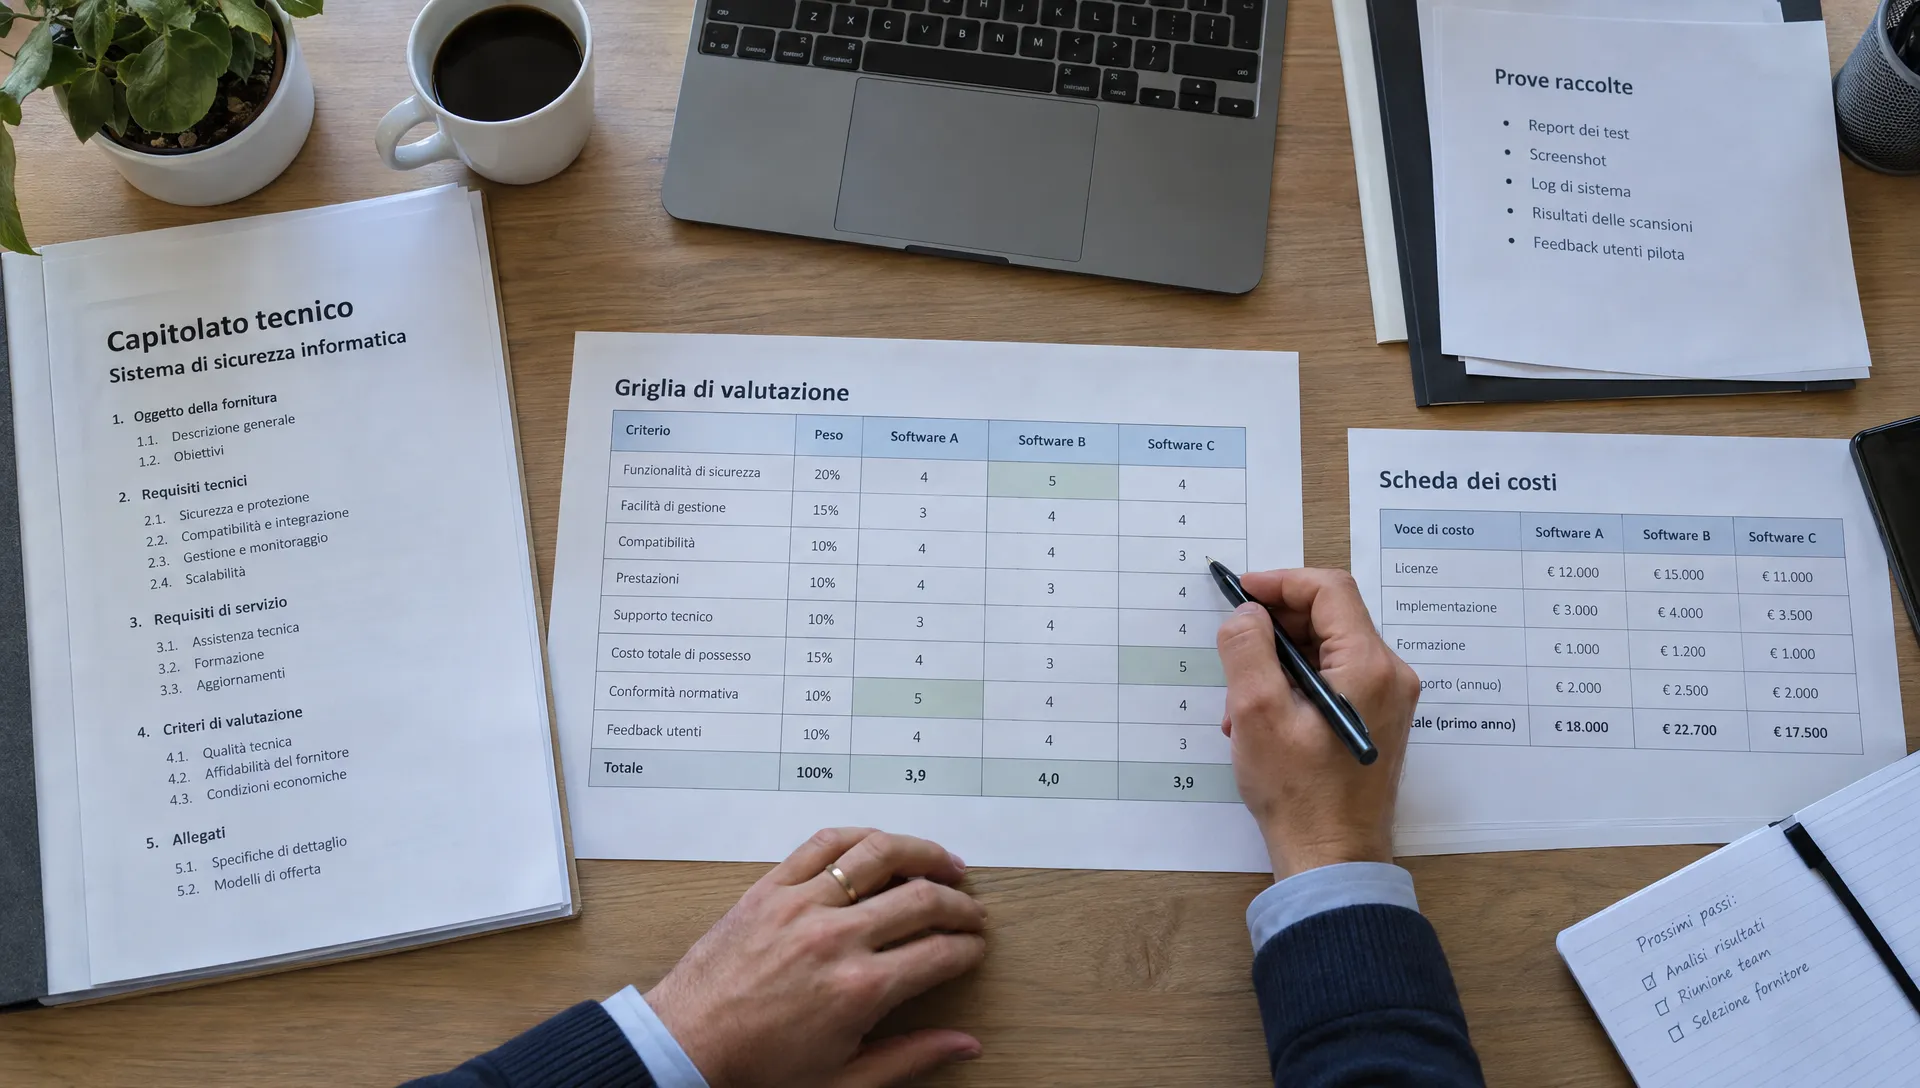
Use the same grid for every candidate. Each row should map a requirement to a test you can perform and the evidence you will retain.
Suggested comparison areas and tests:
- Access and privileges: test different roles and attempt an unauthorized action. Keep test results, role configuration and relevant logs.
- Traceability: change a record and rebuild who changed it, when and what changed. Export the history and version comparison.
- Control execution: assign a control, attach evidence and approve outcome. Preserve the full record with owner, period and result.
- Remediation: open a finding, assign an owner and close it after verification. Link the finding to the corrective action and proof of closure.
- Integrations: import test data and simulate a sync error. Retain import results, error logs and recovery procedure.
- Continuity: review backups and recovery tests for the service. Keep documentation and test outcomes and contractual SLAs.
- Exit and data portability: export records, attachments and reports needed by auditors. Preserve the exported package and the vendor’s exit procedures.
If a function is out of scope for your chosen category, indicate which other tool or process covers it. For every test record whether the response is documented, verified, not available or planned in a roadmap — a future feature is not equivalent to present capability. Save product version, test date and configuration so results remain interpretable later.
Assess the supplier’s operational security, not just product features
Security products can introduce new risks: elevated vendor privileges, access to sensitive data or operational dependencies. Evaluate how the supplier runs the service.
Ask about support staff access controls, account revocation processes and available logs. Check authentication options, role separation and who is responsible for configuration. Confirm whether features shown in a demo are included in the offered contract.
For hosted services, request details on data residency, subprocessors, vulnerability management and incident notification processes. The depth of your supplier review should match the sensitivity of the data and criticality of the service.
Certifications (ISO, SOC reports, etc.) add context but are not a substitute for functional testing. Verify the scope and recency of any certificate and confirm it covers the specific service being bought. If a vendor declines to share sensitive documentation, agree an alternative verification channel such as a confidential review or a verified executive summary.
Translate regulatory requirements into verifiable requests
Regulation gives you justification for requirements, not a checkbox for product marketing claims.
For example, GDPR (Articles 28 and 32) defines liabilities for processors and mandates appropriate security measures. If the vendor will process personal data on your behalf, verify their role, processing terms and the guarantees they provide. Keep the applicable contract, relevant configurations and test results in your procurement file.
If you must meet obligations under NIS2 or similar supply-chain and continuity rules, convert those into operational requests: evidence of incident handling, recovery capabilities and dependency mapping.
Buying software does not by itself discharge regulatory obligations. Compliance requires verifying applicability at the national level and coordinating with internal legal and compliance teams. Your procurement goal is to collect concrete evidence of implemented controls and choices.
Run the same real-world test scenario with every candidate
A vendor-led demo highlights strengths. A comparative trial must replicate a real problem from your environment, using the same data and the same expected results for all vendors.
Use synthetic or properly anonymized data. For an evidence-focused platform, prepare a control with an incomplete proof and a finding to remediate. For a technical protection tool, coordinate a permitted test with your security team.
Introduce deliberate errors and observe how the system handles them
Don’t only follow the happy path. Simulate a missing attachment, a deactivated owner or a failed synchronization. Note who receives alerts, whether the issue remains visible, and how the vendor documents the resolution.
Measure the manual effort required. If the product works only when the vendor’s consultant constantly intervenes, factor that dependency into your cost and risk analysis.
Verify closure, not just opening
A closed finding should preserve the initial problem, the owner, the corrective action, proof of remediation and final verification. Ask to reopen or contest a closure during the test: does the system keep the history, or does it overwrite records?
Use the criteria for verifiable audit evidence (context, covered period, source and link to the control — see /en/blog/evidenze-di-audit). The outcomes of your test should be comprehensible to an auditor who did not attend the session.
Test data export and clarify exit conditions before signing
Portability must be proven in advance. An “Export” button alone does not guarantee that exported data are complete, structured or usable.
Request a sample export that includes records, attachments, identifiers, reports and history. Open those files outside the platform and confirm you can re-link evidence to the corresponding control or remediation.
Distinguish exports intended for auditors (PDFs) from full migrations to another system (structured data and relational links). Contractually clarify timelines for data return, formats, possible assistance fees and data availability after termination. Ask how deletion is handled and whether residual copies may remain with subprocessors. Record all replies in the procurement dossier; don’t rely on verbal assurances.
Calculate total cost of ownership on the same scope
Subscription fees are only part of the cost. Compare bids on identical assumptions: number of users, data volumes and included services.
A practical formula:
Total cost = licenses + onboarding + integrations + internal operational work + extra support + exit costs
For each item split contractual charges from internal estimates and from costs that remain unclear. Onboarding may include setup, migration, role definition and training. Ongoing work may include maintaining integrations, manual evidence collection and export preparation.
A lower subscription may shift effort onto your team; conversely, a more expensive product is not automatically more efficient — operational savings must be demonstrated in the comparative trial.
Check which limits affect price (admin users, additional environments, storage, connectors or specialist support). Use a common time horizon and include a growth scenario. Make all assumptions explicit, especially those the vendor has not yet confirmed.
Score only after collecting evidence
Once you’ve excluded vendors that fail eliminatory requirements, score the remaining candidates with weights agreed across IT, Security, Compliance and Procurement. An example weighting might be:
- Service security and access control: 25%
- Evidence quality and reconstructability: 25%
- Control operations and remediation workflow: 15%
- Integrations and data quality: 10%
- Continuity and support: 10%
- Total cost: 10%
- Reversibility: 5%
Adjust weights for technical protection tools (detection/prevention get a higher share). Use a simple scale (0–3): 0 = not met, 1 = partially met, 2 = met with proof, 3 = exceeded with a documented benefit. Multiply normalized scores by weights and document residual risks and compensating controls.
The final procurement file should include scores, retained evidence, estimated cost, open issues and a clear rationale for the decision, including who accepts remaining risks and how they will be mitigated.
Frequently asked questions
Is a demo enough to choose? A demo can quickly exclude obviously unsuitable products. For critical systems or audit processes you need a hands-on trial with your scenario and preserved results.
What documents should I request before signing? Your specification with vendor answers, the full commercial offer, service terms, relevant security documentation and trial outcomes. If the vendor processes personal data on your behalf, include the applicable data processing conditions.
How do I compare a security product with a compliance platform? Start from the result you expect. Protection tools detect or block threats; compliance platforms organize responsibilities, controls and proofs. Evaluate how the two integrate when you need both execution and demonstrable controls.
Who should approve the purchase? Stakeholders responsible for each requirement must validate their verification. The final decision should follow internal delegation rules and document economic terms, residual risks and operational responsibilities.
Apply this method to your NIS2 perimeter
If you are evaluating a platform to manage NIS2 controls and evidence, try AuditReady against your operational scenario at /en/auditready/lp/nis2. Bring a real control, a finding and the expected outcome: compare ownership, traceability, remediation and export against your specification, and avoid conflating evidence management with technical protection of systems.
audit-ready evidence pack demo / not legal advice