Audits rarely fail because a single document is missing. More often, findings stem from controls, responsibilities and evidence being handled only at the last minute — when reconstructing decisions, approvals and operational activities is already difficult. True prevention begins long before the auditor arrives: it’s built into how your organization works week to week.
Preparing for an audit means turning it from an extraordinary event into a natural verification of an orderly system. Practically, that requires knowing which requirements apply, which controls address them, who performs those controls, what evidence is produced, and how deviations are remediated. This is the same mindset behind the idea of compliance as an ongoing system rather than a point-in-time task (see /en/blog/compliance-sistema-continuo).
Why non‑conformities usually originate before the audit
An audit highlights a problem; it doesn’t usually create it. When auditors record non‑conformities, the root causes are typically earlier: ambiguous interpretation of requirements, unassigned controls, evidence stored without context, or organizational changes not reflected in documentation.
This applies across frameworks such as GDPR, NIS2, DORA, ISO 27001 and the AI Act. Specific obligations differ, but the operational principle is constant: every requirement must be translated into activities that are observable and provable. Without that translation, auditors cannot see a logical chain from rule to risk to control to evidence.
Prevention, therefore, is practical: reduce ambiguity rather than simply “do more compliance.” An organization that can say who does what, how often, where the proof lives and which risk is mitigated will face far fewer surprises during an audit.
Map requirements to controls and owners
Each applicable requirement should correspond to an operational control. A piece of regulatory text alone is hard to verify; a control describes expected behaviour, frequency, owner and observable result.
Start the mapping from a realistic perimeter: which processes handle personal data? Which digital services are critical? Which third parties affect operational continuity? Which functions approve access, incidents, changes and processing activities? Without that baseline, checklists can mistakenly cover low‑priority areas while leaving critical gaps.
Typical mapping questions and expected evidence:
- GDPR / privacy: Are purposes, legal bases and roles documented and current? Evidence: register of processing activities, DPIAs when required, privacy notices. Red flag: new processing activities not recorded.
- NIS2 / cybersecurity: Are incidents classified, managed and reviewed? Evidence: tickets, incident reports, escalations, lessons learned. Red flag: incidents closed without root cause analysis.
- DORA / ICT third parties: Are critical suppliers assessed and monitored? Evidence: inventory, contracts, SLAs, periodic assessments. Red flag: critical contract without a responsible owner.
- ISO 27001 / access management: Are access rights granted, reviewed and revoked traceably? Evidence: review reports, approval records, revocation logs. Red flag: orphaned accounts or excessive privileges.
Define owner, frequency and acceptance criteria
Many non‑conformities arise not from the absence of controls, but from inconsistent execution. A control may exist on paper, but no one knows when it must be performed, who validates it or what counts as acceptable evidence.
Each control should have at minimum:
- an owner responsible for execution and evidence,
- a defined frequency (daily, quarterly, on change, etc.),
- explicit acceptance criteria (what constitutes success).
For example, a quarterly access review should document who performed it, the scope of systems reviewed, anomalies found, access revocations performed and where the closure evidence is stored. This removes grey areas the auditor would otherwise have to interpret.
Capture evidence as it is produced
Non‑conformities become more likely when evidence is gathered only right before the audit. Hasty searches for emails, screenshots and tickets often miss the context that makes proof verifiable.
Useful evidence is not just a file: it must indicate which control or requirement it supports, when it was produced, who approved it and what period it covers. An access report without extraction date, application scope or review outcome may be insufficient even if it technically contains the right data.
Adopt a minimum standard for evidence quality. Each item should identify:
- the related control or requirement,
- the covered period or triggering event,
- the responsible person,
- the verification result,
- any corrective actions opened or closed.
For a practical guide on structuring evidence, see /en/blog/evidenze-di-audit.
Monitor operational signals before they become formal issues
Operational indicators help detect non‑conformities early. You don’t need dozens of metrics — a few signals tied to critical controls, observed regularly, are enough.
Useful signals include: proportion of overdue control executions, number of evidences rejected during review, incidents without root cause analysis, critical suppliers lacking recent assessment, or access exceptions open past their expiry. These signals don’t prove non‑compliance on their own, but they highlight where to look before an auditor does.
When a signal recurs, ask the right questions: is the control frequency realistic? Are resources missing? Is evidence collection too complex? Or is the control poorly designed? Short, decision‑oriented reviews help convert signals into corrective actions rather than firefighting.
Validate the design of controls, not just execution
A control can be performed consistently and still fail to satisfy the requirement if it isn’t designed to mitigate the right risk. Showing that “something was done” is not enough if that something doesn’t address the regulator’s objective.
Design review asks different questions than execution review: Does the control cover the intended risk? Is the frequency proportionate? Does the owner have adequate authority? Is the evidence independently verifiable? Are exceptions properly managed?
For critical controls — access management, incident response, privacy governance, business continuity and vendor management — perform a design assessment in advance. See /en/blog/control-design-assessment for approaches to reduce structural weaknesses before they become formal findings.
Run small, regular internal audits
Simulate the external audit on a limited scope with mini internal audits. A monthly or quarterly review of one process will expose gaps an annual check would reveal too late.
Pick a requirement, select related controls, verify available evidence and interview the owner. The goal isn’t to create pressure, but to measure real maturity. If evidence is unclear, controls aren’t executed, or owners can’t explain processes, you still have time to remediate.
Treat mini audits with the same discipline as external ones: record scope, criteria, results, findings, corrective actions and governance decisions. They become governance evidence showing you continuously monitor your compliance posture.
Manage remediation so issues don’t return
Every internal finding should become a tracked corrective action that addresses root cause — not just a quick upload of a missing document. Documents are often symptoms of deeper process gaps.
A complete remediation record should include: root cause, assigned owner, due date, closure evidence and a verification of effectiveness to confirm the problem didn’t recur.
Elements that make remediation effective:
- Root cause analysis to avoid superficial fixes
- Clear owner to ensure accountability
- Deadlines to prevent findings from lingering
- Closure evidence that demonstrates completion
- Effectiveness check to confirm lasting resolution
Review remediation frequently with focus on the highest risks and sensitive obligations. Audits don’t expect zero problems in complex organizations; they expect evidence that issues are detected, assessed, corrected and managed.
How AuditReady supports prevention
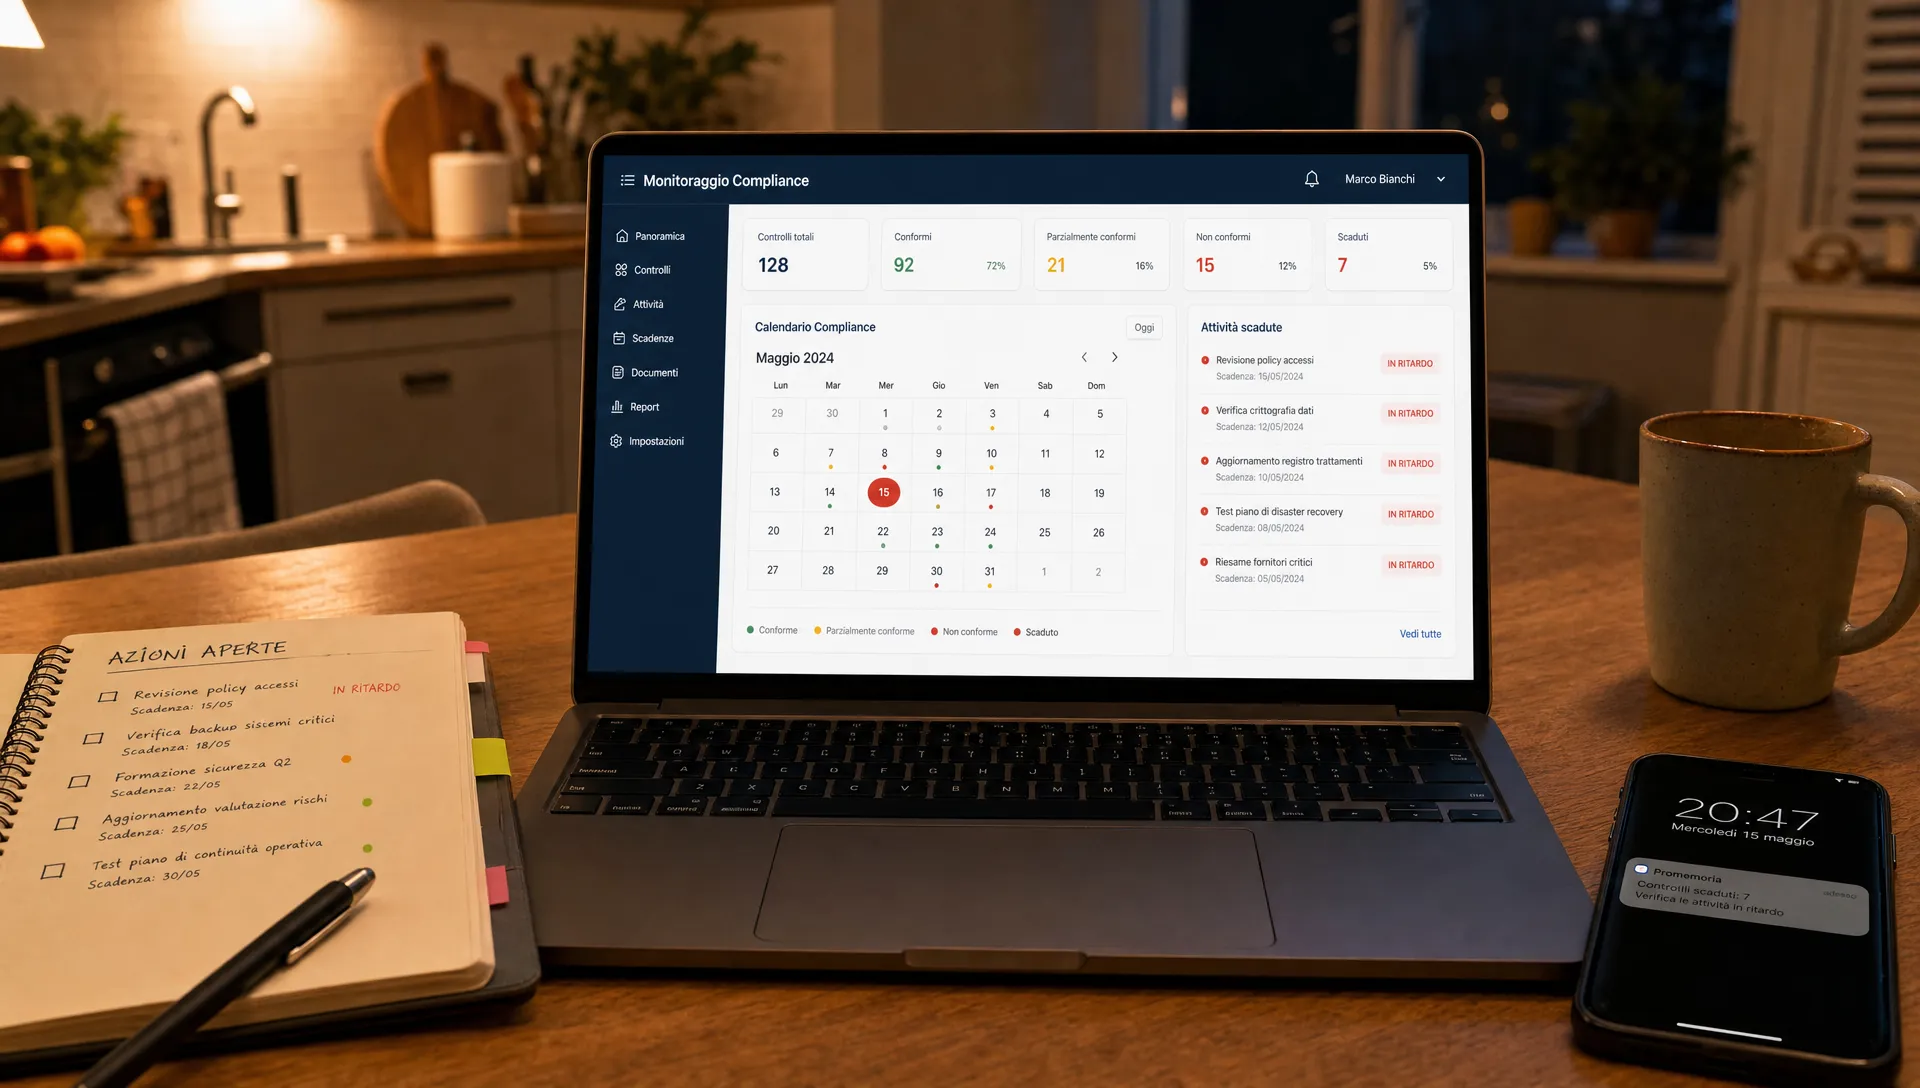
AuditReady helps prevent non‑conformities by centralizing controls, evidence, risks, incidents, privacy registers and governance in a single operational workspace. This reduces fragmentation from folders, spreadsheets, emails and siloed tools.
In multi‑framework environments, the same evidence often supports multiple obligations. A structured platform links controls, owners and proofs without duplicating work. Features such as control and audit tracking, risk and incident management, privacy register workflows, role‑based access, secure document sharing and structured exports let teams keep order well before an audit.
The principal advantage is not just better storage, but making the system interrogable: when an auditor requests proof, teams can quickly reconstruct scope, owners, control status and linked evidence. That’s when compliance shifts from document collection to verifiable operations.
Common mistakes to avoid pre‑audit
- War room mentality: starting frantic evidence collection weeks before the audit. This yields partial traces that require interpretation.
- Policy centricity: relying on policies alone. Auditors look for evidence that policies were applied, not just that they exist.
- Ignoring exceptions: exceptions can be acceptable if approved, temporary and monitored. Untracked exceptions without owners or deadlines are weaknesses.
Practical FAQs
How far in advance should prevention begin? Ideally, prevention is continuous. If an audit date is set, start a structured review at least several weeks ahead, prioritizing critical controls, missing evidence and open corrective actions.
What’s the difference between an internal finding and a formal non‑conformity? An internal finding is an issue the organization detects itself. A formal non‑conformity is identified by the external auditor against defined criteria. Finding issues internally allows time to fix them before they become audit results.
Are checklists enough? Checklists help avoid omissions, but they’re insufficient alone. Effective readiness requires assigned controls, verifiable evidence, clear responsibilities, exception handling and tracked remediation.
How do you prove a control is effective? Show that the control is designed to mitigate a specific risk, is performed at the defined frequency, produces consistent evidence and prompts corrective actions when anomalies arise.
Reach the audit with a verifiable system
Preventing findings isn’t about chasing perfect documentation. It’s about building a system where requirements, controls, risks, owners, evidence and remediation are connected and current. When that structure exists, the audit becomes confirmation of ongoing work rather than a last‑minute scramble.
If you want to organise evidence, controls and responsibilities in a workspace tailored for operational compliance, discover AuditReady at https://audit-ready.eu and evaluate how to make your audit preparation more traceable, orderly and sustainable.