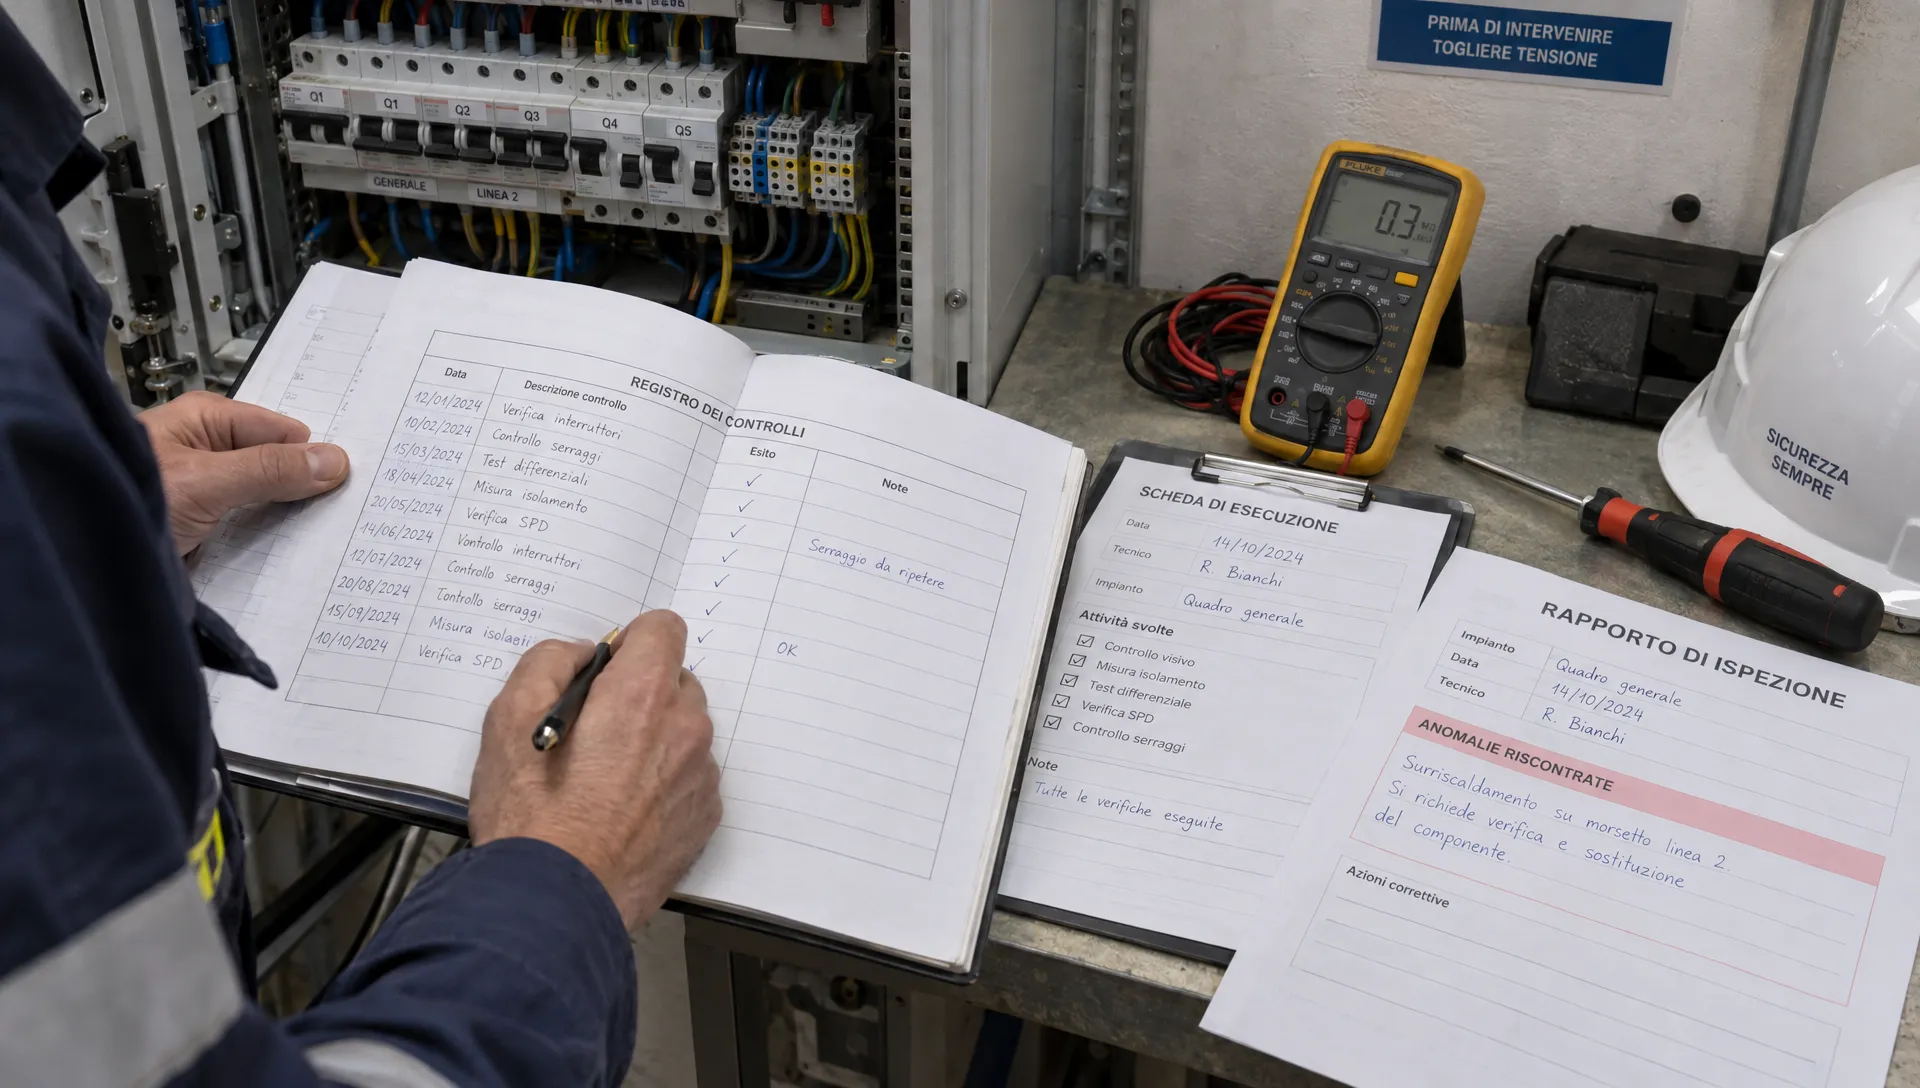
A deadline tracker only strengthens control when it captures not just what was planned, but what was done, the outcome, and the evidence that supports it. For a DPO, CISO or internal auditor, getting a reminder is useful — but it’s not proof that a review was completed correctly. The difference between an activity that was ticked off and one that is verifiably closed comes down to the closure process, not the number of notifications.
Why a shared calendar stops being enough
A shared calendar works for a small set of simple checks owned by one person and supported by easy‑to‑find evidence. It becomes fragile when separate people prepare evidence, execute the check and accept the result.
You notice the weakness during an audit: to justify a completed task you need to reassemble emails, attachments and decisions made outside the calendar. You also see items marked as closed while a report is still missing or an anomaly remains open.
Continuity matters too. When the responsible person changes role, the new owner must quickly see which checks are overdue, which were deferred and whether previously supplied evidence covered the full period. If those answers live in someone’s memory, the calendar is no longer a reliable control tool.
What a deadline system must track to add control
The real improvement is connecting deadline, execution and evidence acceptance. These are separate moments and should remain distinct, even if they occur on the same day.
A check can be executed on time but poorly documented; or it can produce a failing result that requires remediation. Simply marking an item “completed” hides information auditors and risk owners need.
At minimum the system should record distinct dates and what they mean:
- Reference deadline: when the check was originally due — used to assess punctuality against plan.
- Internal target date: an operational earlier date to prepare documents and allow review before the deadline.
- Execution date: when the check was actually carried out — separates real activity from planning.
- Validation date: when the expected reviewer accepted the evidence — proves closure did not depend only on the executor.
Also record the period covered by the check. A file uploaded in October may refer to the previous quarter; upload date alone does not prove the current period was reviewed.
Handle postponements without erasing backlog
A system loses value if moving a date makes an overdue item disappear. Rescheduling should keep the original deadline visible, the new date, the reason and who authorized it.
Separate the act of postponement from risk acceptance. Changing a date does not mean the risk from a missed check was reviewed. For critical processes, document any temporary compensating measures and the person who approved the change.
Distinguish internal plan adjustments from regulatory or contract deadlines. Legal or contractual obligations should be tracked and evaluated by the appropriate functions; changing an internal timeline is a management decision, not automatic regulatory relief.
Example: reviewing access to personal data
Imagine a quarterly review of user access for an application that processes personal data. Quarterly frequency is a choice of the internal control plan — not a universal GDPR requirement.
The IT owner exports the user list and privileges. The process owner validates whether access rights are still required. The privacy lead assesses whether the evidence demonstrates scope and actions taken.
A good deadline tool shows the difference between “list received”, “accesses reviewed” and “result accepted”. To close the review you should capture at least the application scope, extraction date, selection criteria and the review outcome. If an access must be revoked, keep the revocation request and confirmation linked to the original check.
The GDPR accountability principle (see Regulation (EU) 2016/679) requires data controllers to be able to demonstrate compliance. A deadline tracker supports that demonstration — it does not replace it. For more on linking controls and evidence see our audit model in the public blog: /en/blog/gdpr-audit-conformita-dimostrabile.
When external technical expertise is required
The same distinctions apply to inspections of equipment or technical assets: booking an external technician is not the same as having the inspection result. If specialised skills are needed, the plan must allow for technician availability, access to equipment and time to receive and validate the report.
External engineering and inspection firms illustrate this workflow: the calendar should show the inspected object, the internal owner and the expected deliverable. An appointment confirmation is proof of planning, not proof of outcome.
How to test a deadline system before you buy
A meaningful evaluation uses real, problematic cases rather than a demo filled with on‑time completions. Prepare a small sample of actual checks (redacting confidential data where needed) and ask the vendor to reconstruct the full lifecycle.
Include these test scenarios:
- Overdue review: the deadline passed, the owner is known and suitable evidence is still missing; the overdue status must remain visible.
- Rejected evidence: the task was executed but the document doesn’t cover the required scope; it should remain open until adequate evidence is supplied.
- Owner change mid‑cycle: the responsible person leaves; the system must preserve previous responsibilities and show the handover.
- Authorized postponement: a new date exists but the original deadline, the reason and the recorded decision must remain consultable.
Ask what an auditor would see: they should be able to follow the sequence without chasing explanations. An export of task titles is not enough — you need links to evidence and a readable chronology of decisions.
These are evaluation criteria, not assumptions that every product implements them. Choosing an evidence‑first internal audit tool starts with the ability to verify the process through evidence. See our guidance on selecting software for internal audit in the public blog: /en/blog/software-audit-interno.
Measure outcomes, not notification volume
To know whether a tracker improves your process, compare consistent indicators before and after adoption. The number of reminders sent measures system activity, not audit effectiveness.
Useful indicators include:
- Share of checks with accepted evidence by the reference deadline (over the total due in the period). Don’t remove deferred tasks from the denominator, or improvements will be illusory.
- Time between execution and validation. A growing gap suggests bottlenecks in evidence quality or reviewer availability, not in execution.
- Age of backlog and number of reopens for incomplete evidence. Interpret these with process criticality: one overdue control on a critical process can be more significant than many low‑risk administrative items.
Don’t invent universal thresholds. Set internal targets that align with risk and document how you chose them.
Common mistakes that break trust in the schedule
- Creating the next recurrence before the previous cycle is closed. If September’s review is open, December’s task must be distinct; opening a new item doesn’t solve the missed control.
- Confusing check closure with remediation closure. A check can be marked with a failing result while corrective work is still in progress; both states should be visible with owners and evidence.
- Attaching a document without specifying version and scope. A report tied to a different system or period can appear sufficient if only the filename is inspected, but it doesn’t prove the required execution.
- Ignoring out‑of‑cycle events. Supplier changes, incidents or major service modifications may require reviews outside the calendar; the process must provide how to open and link those checks to the triggering event.
FAQ
Q: Can a shared calendar be enough? A: Yes, for a small number of simple checks — provided responsibilities, evidence and decisions remain accessible. The limit appears when the calendar records dates but not validated outcomes.
Q: Does a deadline tool prove compliance automatically? A: No. It can make activity verifiable, but compliance still requires adequate controls, relevant evidence and documented decisions. A reminder or a “completed” flag is not a substitute for proof.
Q: When is a check considered closed? A: When closure criteria for that check are met: documented execution, correct scope, recorded result and the required validation. Remediations may have their own lifecycle but must remain linked.
Q: Do all checks need to be recurring? A: No. Some are periodic, others are event‑driven. Distinguish the two and justify frequencies or triggers based on process, risk and applicable obligations.
Connect checks to the audit dossier
AuditReady centralises evidence with ownership, versioning and audit trail, alongside controls, risks and remediation tracking. The operational goal is to preserve proof of the work done, not merely to remind people when to do it.
To see this approach applied to privacy reviews, evaluate AuditReady’s GDPR audit pack: /en/auditready/lp/gdpr.
audit-ready evidence pack demo / not legal advice