A scheduling tool becomes truly useful for audits when it records not just what’s due and when, but who must act, what must happen first, and which evidence proves the work is complete. The common operational challenge is rarely remembering an audit date — it’s arriving at that date with controls performed, evidence validated, and any open issues clearly described.
To coordinate compliance teams, IT and process owners, separate three distinct phases: execution of the control, validation of evidence, and final review. Below is a practical method to connect those phases, manage delays and changes without losing the decision history, and produce a verifiable evidence package on the agreed date.
Distinguish obligation dates, internal frequencies and audit appointments
Before adding a deadline to a schedule, identify its origin. A date mandated by a legal or regulatory obligation (GDPR, NIS2, DORA, ISO requirements) should be treated differently from an internally chosen frequency based on risk or a date negotiated with an auditor.
Regulations such as the GDPR (see principles and accountability) require organisations to demonstrate compliance and to review and update measures when necessary. These references guide what must be demonstrable, but they do not prescribe a universal checklist of monthly or quarterly checks.
Use a short taxonomy to capture why a date exists and what to record for each:
- Applicable obligation: record source, triggering conditions and how the deadline is calculated. Assign legal or compliance ownership to verify applicability.
- Audit programme: record scope, period under review and delivery deadline. Plan backwards from delivery to collect and validate evidence.
- Internal frequency: record the risk assessment and the rationale for the interval. Reassess when the context changes.
- Corrective action: link the finding, priority and expected outcome. Assign an owner and a verification criterion.
In the scheduling tool, the rationale for a date must remain accessible alongside the control: a generic “due date” field is not enough to explain why the work was required at that moment.
Note: this organisational classification is not legal advice. When a deadline depends on a legal interpretation, link to the assessment performed by the competent party instead of attempting to codify legal applicability into an automated rule.
Configure three dates per control and explicit dependencies
For each control cycle, separate at least these three milestones: execution deadline, validation deadline, and review date. They may coincide for simple activities, but separating them exposes the handoffs that usually get lost in email threads.
- Execution: the owner performs the control and uploads evidence.
- Validation: a validator confirms the evidence is sufficient and relevant.
- Review: the reviewer assesses findings, open issues and decisions (accept, remediate, accept with exceptions).
Record for each activity: the control it supports, period covered, scope, execution owner, validator, dependencies, and acceptance criteria. Replace vague tasks like “check access” with precise instructions such as “review administrative accounts for systems in scope, document outcomes and required revocations.”
Dependencies must be concrete: the access review may depend on an up-to-date user inventory and confirmations from system owners. If a dependency is missing, mark the activity as blocked rather than merely late.
The schedule should store both planned and actual dates for each milestone so you can distinguish execution problems from validation bottlenecks.
Maintain a reconstructable audit trail for assignments, changes and approvals (author, timestamp, and content of change). See related guidance on maintaining an audit trail at /en/blog/audit-trail-best-practices.
Build the plan backwards from the auditor delivery date
The auditor’s date should not become the deadline for every control. If evidence arrives on the audit day, there is no time to validate it or fix gaps.
Example (illustrative, not regulatory): internal audit scheduled for 30 November with a required evidence package. Plan backwards with realistic buffers:
- Evidence collection: 10 November — gather evidence covering the requested period.
- Validation: 17 November — accept or reject evidence with reasons.
- Remediation review: 20 November — assign corrective actions for findings.
- Package consolidation: 25 November — select versions and declare open issues.
Adjust buffers to complexity: an already-available export may need little time; a review involving multiple sites or third‑party providers will have additional dependencies.
The scheduling tool should make this sequence visible so that on-paper punctual tasks do not produce a late audit package.
Consolidation does not stop operational controls. It identifies the versions and state of evidence included in the package. If new evidence arrives after consolidation, record it as an identifiable addendum rather than silently replacing previously validated documents.
Agree with auditors in advance which period and scope must be demonstrated — a correct but out-of-period evidence file does not satisfy the requirement.
Manage delays and rescheduling without erasing the history
Rescheduling can be necessary. Overwriting the original date without explanation makes it impossible to tell the difference between an authorised reschedule and an activity that fell behind.
Preserve the original date, the updated date, the reason for change, the approver and the impact on dependent activities. If the delay creates risk, record the decision on risk treatment and any temporary compensating controls.
Example: an access review is delayed because the system inventory is incomplete. The response should include assigning completion of the inventory and identifying how the unverified portion of the scope will be covered in the meantime — not just moving the review date.
A well-governed schedule uses meaningful states (open, blocked, in validation, completed) rather than just colour codes that do not indicate required actions.
Escalation must target a named decision‑maker with an expected decision. Asking the process owner to reallocate resources or a risk owner to assess consequences is more effective than sending the same reminder to a broad distribution list.
A finding is not closed by publishing a remediation plan alone. Closure requires evidence that the fix was implemented and verification against the acceptance criteria. Until then, the finding must remain visible in the audit package.
Trigger reviews when context changes
Periodic recurrence does not catch every relevant change. A new supplier, a migration or a process change may render a previously valid control ineffective.
Define triggering events that require an early assessment: scope change, an incident related to the control, a failed check, or introduction of new systems. Not every event needs a full audit; assign a responsible person to evaluate which controls are affected and which evidence must be updated.
For cross‑functional initiatives (marketing launches, platform changes or product experiments), involve compliance and IT before release. If a project introduces a new vendor, tool or data processing activity, identify affected controls and plan necessary updates in the schedule ahead of the go‑live.
In the scheduling tool, link extraordinary activities to the event that spawned them and to the routine cycle they touch. Do not delete the regular cycle for convenience — document whether the extraordinary check covers only the new component while the periodic review still covers the whole scope.
Define when an activity is truly complete
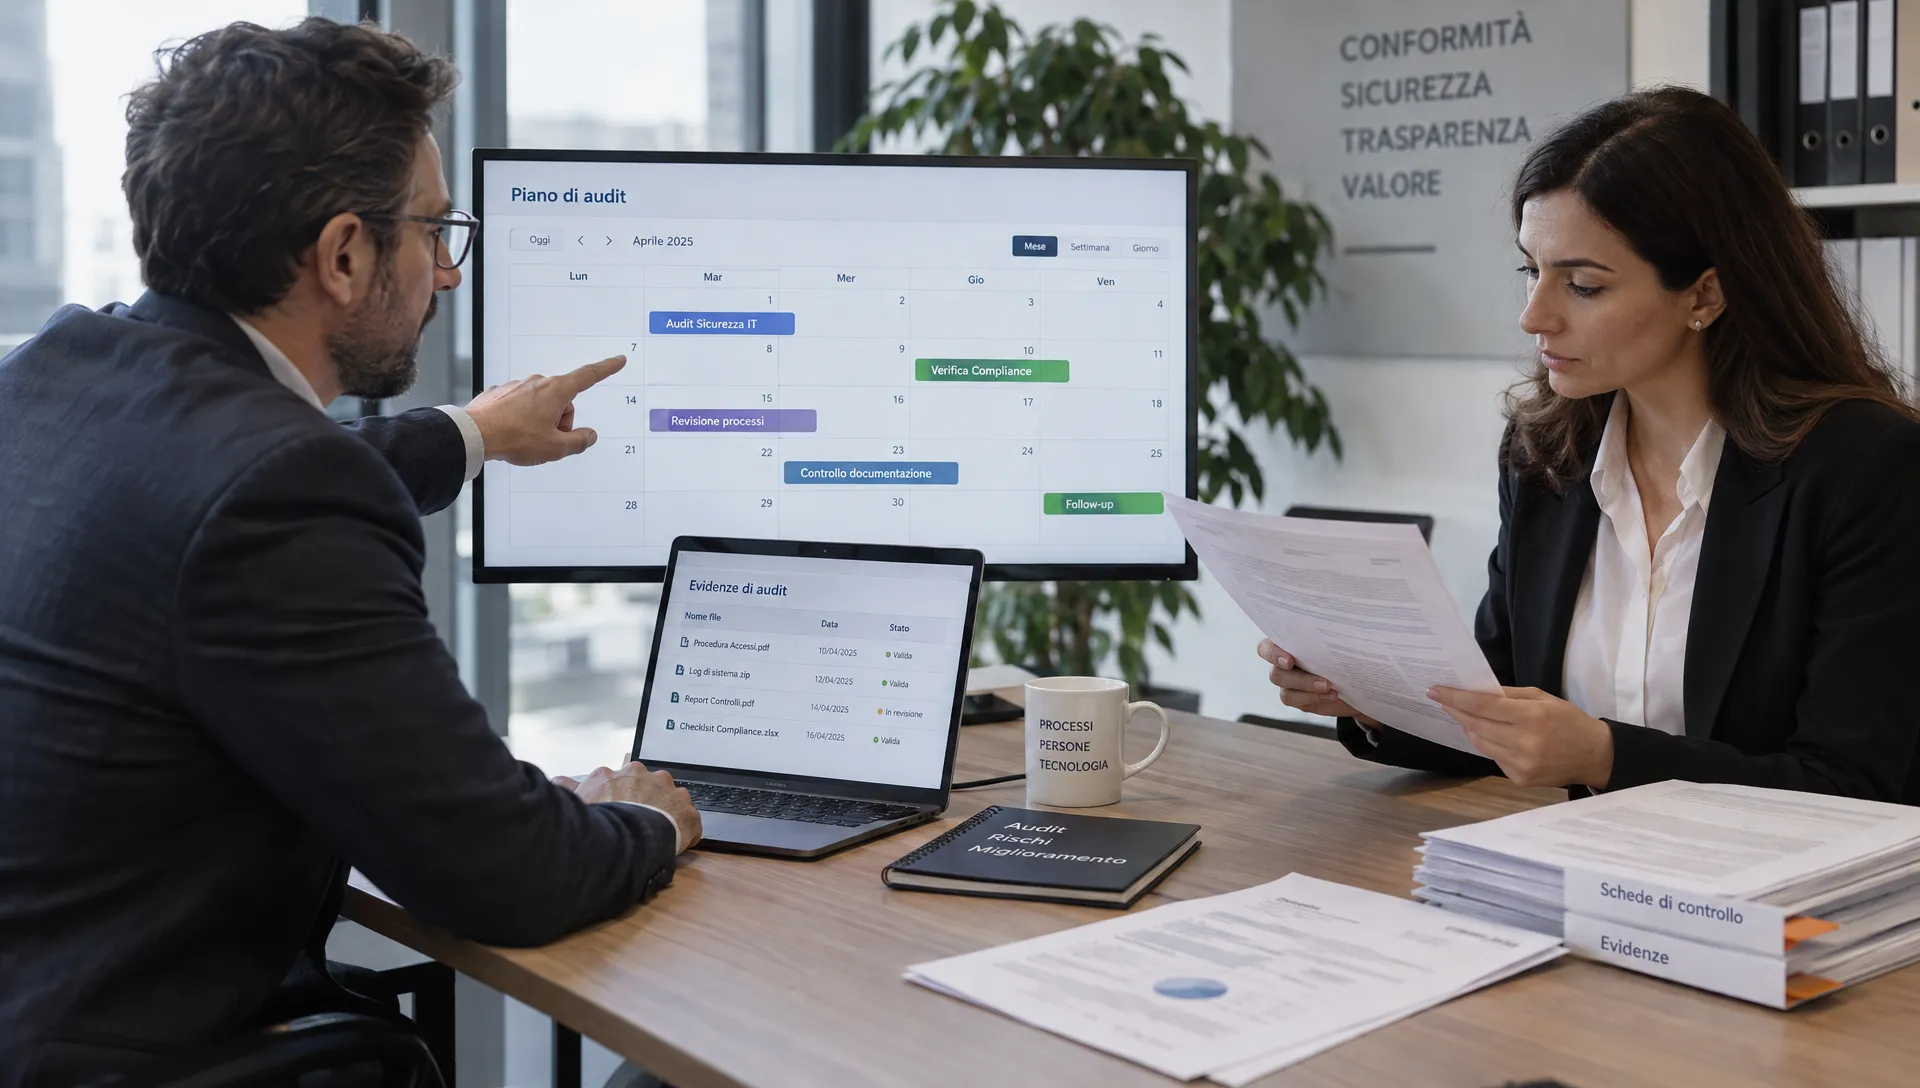
“Completed” should mean a verified outcome, not merely that a file was uploaded. Before starting the cycle, agree what makes evidence acceptable and who will evaluate it.
For an access review, acceptance criteria might include an inventory snapshot for the agreed date, list of systems in scope, results of the checks and linkage to required actions. These criteria should be operationally defined for each control, not assumed.
Link completion status in the schedule to these conditions and keep execution separate from remediation resolution.
A control may be performed correctly yet reveal a problem that remains open. In that case, record the outcome, link the finding and trigger remediation. Do not mark everything as “compliant” simply because the planned activity was executed.
When selecting audit evidence, prioritise period, scope, provenance and version. A well‑formatted document that cannot be traced to the reviewed activity does not prove that the control worked. See guidance on gathering audit evidence at /en/blog/audit-evidence.
In the final review, show separately: activities completed with accepted evidence, activities performed with open findings, and activities not performed or not demonstrable. This clarity helps auditors understand the true state without reconstructing it from emails.
Evaluate the scheduling tool with an operational test
Before choosing a tool, create a short test scenario: one audit, several controls, a rejected evidence item and a rescheduled deadline. Use test data and exercise the entire process, not just the calendar view.
A proper evaluation should demonstrate you can find blocked activities, reconstruct date changes, and trace from the auditor delivery to the actually accepted evidence.
During testing, change the owner of a control in flight and confirm the previous assignment remains auditable while the new owner sees the period, acceptance criteria and remaining work. Reject a document and verify it’s clear who must fix it and what deadline remains valid.
Export the auditor package and confirm it identifies control, period, outcome, evidence versions and open findings without relying on ad‑hoc explanations from owners.
AuditReady centralises evidence with ownership, versioning and an audit trail, and manages controls, risks, findings and remediation. Those core functions address evidence handling and outcomes. Recurrence management, dependency modelling, notifications and integrations with calendar tools are additional requirements you should explicitly test; do not assume they are present simply because a platform supports compliance management.
FAQ
Q: Can a shared calendar be enough?
A: For simple appointments, yes. When you need to link periods, owners, validations and evidence versions, check whether the calendar lets you reconstruct the full path or whether important information stays scattered elsewhere.
Q: How often should controls be scheduled?
A: There’s no single interval. Distinguish applicable legal obligations from internal frequencies and document the rationale for the latter based on risk, changes and past outcomes.
Q: How do you avoid losing tasks after an audit closes?
A: Keep findings, remediation and follow‑up checks linked to the next cycle. The scheduling tool should carry open activities forward without erasing their history when an audit is closed.
Q: Can a control be closed while remediation is still open?
A: Yes — if the control was performed and validated against the agreed criteria. The finding and its remediation remain open and must be tracked separately.
Bringing the schedule into the evidence process
To test this approach on a concrete scope, explore AuditReady for GDPR evidence management at /en/auditready/lp/gdpr. Start from a real control and map how owner, period, evidence, validation and remediation connect: this workflow, more than the number of reminders, makes compliance demonstrable.
audit-ready evidence pack demo / not legal advice