A document management system can be just a place to store files — or it can be a tool that makes versions, permissions and evidence defensible during an audit. The difference is not how many folders you have, but whether you can demonstrate who uploaded a file, which version was valid at a given date, who approved it, who had access, and which control or requirement it supports.
This article translates common audit needs into practical document controls for privacy officers, compliance managers, CISOs, IT leads, internal auditors and consultants who must produce verifiable evidence. It does not provide legal advice.
Why document management matters for audits
Auditors don’t just want the latest copy of a policy. They want to reconstruct the lifecycle of the evidence and link it to requirements and controls (GDPR, NIS2, DORA, ISO standards, corporate governance models, etc.). In a regulated context, every file should answer the audit question: which obligation or control does this prove?
Ask not “where do I save the file?” but “if an auditor asks why this evidence is reliable, what do I show?” A good answer demonstrates four things: context, integrity, accountability and status. A lone file called procedure_final_v3.pdf is readable, but usually insufficient to explain responsibility, change history and remediation.
For a deeper view on building chains of proof, see the concept of verifiable audit evidence in related posts: /en/blog/evidenze-di-audit
Versioning: what must be provable
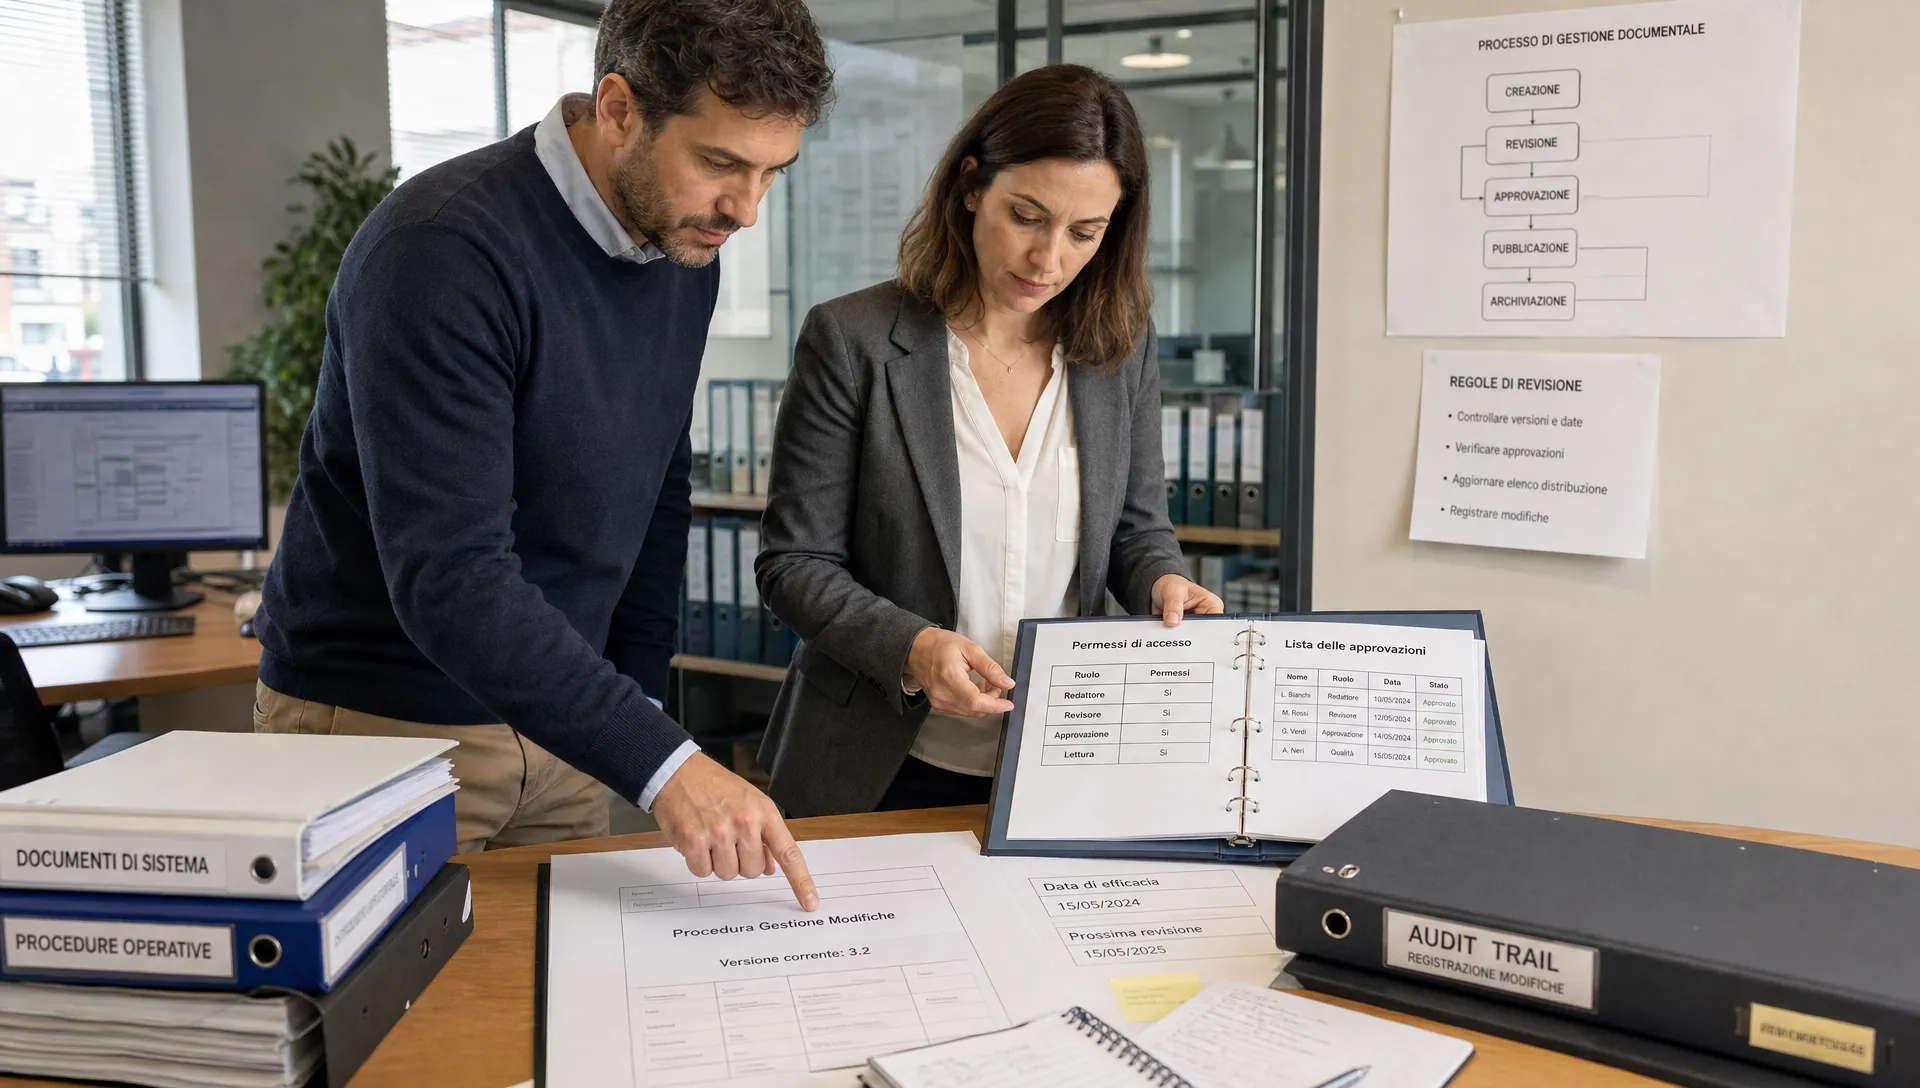
Version control is where a live document becomes defensible evidence. Auditors need to know which version applied during the period under review and why later versions replaced earlier ones.
A versioning control should let you answer:
- Which version is currently valid?
- Who created or modified a version?
- What changes were introduced?
- Who approved publication?
- When did the version become effective?
- Which version was valid during an incident or audited period?
The most common failure is missing historical versions. If a policy changed in March but the audit concerns January–February, inability to retrieve the January version weakens your position.
Minimum metadata for auditable versions
Rather than depending on file names, enforce a small set of mandatory metadata fields consistently. A simple structure is enough if applied reliably:
- Document ID — eliminates ambiguity (e.g., PRIV-POL-ACCESS-001)
- Version number — reconstructs evolution (1.0, 1.1, 2.0)
- Status — draft, approved, archived
- Owner — responsible function or role (CISO, DPO, HR)
- Effective date — when the version takes effect
- Change rationale — links update to a risk, finding or regulatory requirement
- Approver — who validated the version
- Linked control — which compliance control or requirement this documents
These are not bureaucratic details: they reduce time spent reconstructing past decisions and make evidence easier to defend.
Permissions: favor clear responsibility over broad access
Permissions affect credibility as much as confidentiality. If many people can modify a document without controls, demonstrable integrity and accountability suffer.
Design permissions around roles rather than individual files. Each document should have at least one owner, a group of contributors, defined approvers and a read-only audience where appropriate. Administrative privileges must be restricted, justified and periodically reviewed.
A practical permission matrix might look like this:
- Owner of control: read, edit, propose approval, export; deletion only via workflow
- Approver: read, approve, export
- Contributor: read, edit drafts
- Internal auditor: read, export when authorized
- Supplier: limited upload/attachment access, no deletion
- System admin: technical access logged and reviewed
Answering “they have access because they’re on the team” is weak. A better answer is “they have access because they’re contributor to control X until remediation Y is closed.”
Audit trail: make the history usable
Versioning and permissions only help if their events are recorded and retrievable. The audit trail should capture key events such as creation, modification, approval, download, permission changes, archiving and authorized deletion.
An auditor does not need raw, unreadable logs. The trail must be filterable by document, owner, control, period and event type so you can demonstrate, for example, that a change after a finding was approved and the remediation executed.
For guidance on practical logging, see best practices on audit trails: /en/blog/audit-trail-best-practices
Example: updating an offboarding policy after a finding
Consider an internal finding that former employees’ accounts remained active. The remediation requires updating the offboarding procedure, strengthening periodic access reviews and collecting evidence of the first execution.
An acceptable evidence chain would include:
- The original finding with date and responsible person
- The previous offboarding procedure (version X)
- The updated procedure with the change rationale
- Approval record for the new version
- Evidence of the access review being executed (reports, tickets)
- Closure of the remediation with owner and date
A document system only helps if it enforces or encourages capturing these steps in one place instead of scattering proof across email, chat and local drives.
Operational workflow to build an evidence pack
An evidence pack should not be assembled at the last minute. It should emerge naturally from routine work when simple rules are applied whenever a compliance document is created or changed.
A recommended flow:
- Create or update the document against a control or requirement (not an arbitrary folder)
- Assign owner, contributors and approver before collecting evidence
- Lock the approved version and keep prior versions according to retention rules
- Restrict edit permissions to roles in the workflow
- Link findings and remediations to the same document record
- Produce auditor-friendly exports including essential metadata and control references
This approach reduces reliance on individual memory and makes the document part of a control lifecycle. For software-focused workflows, see: /en/blog/software-audit-interno
What to include in an auditor export
Exports should be curated, not a dump. For each document, include at minimum: ID, title, version, status, owner, effective date, linked control and last approver. If the auditor needs to verify an operational measure, include execution evidence: reports, screenshots, synthetic logs, closed tickets or attestations — each with owner and date. Distinguish supplier-provided evidence from internally produced evidence and record the collection channel.
Common mistakes and how to prevent them
Frequent pitfalls:
- Treating the document system as a neutral deposit where each team organizes files differently
- Confusing “latest version” with “version that was valid at a given time”
- Relying on inherited folder permissions that are too broad or too restrictive
Avoid these by scheduling short, regular checks that produce traceable results.
Suggested periodic checks:
- Review document owners for critical items (quarterly or semiannual)
- Review access to sensitive folders (quarterly)
- Verify approved versions before audits or reviews
- Sample audit trails for anomalies (quarterly)
- Close document-related remediations (monthly if findings open)
Adjust frequency to risk, scope and applicable frameworks; document and justify your choices.
How AuditReady supports the process
AuditReady centralizes evidence, controls, risks, incidents, privacy registers and governance in a single workspace. In document terms, it connects proofs to controls and responsibilities while preserving versions, owners, audit trails and auditor-ready exports.
This does not replace the need to define roles, policies and access criteria, but it reduces fragmentation caused by scattered shared folders, spreadsheets and email attachments where evidence exists but is not easily traceable or linked to a control.
If you are preparing GDPR-related evidence and want to move from scattered folders to structured controls and traceable proofs, consider AuditReady as a practical platform to build organized evidence packs: /auditready/lp/gdpr
FAQ
Is a document management system enough to prove compliance? No. You need processes that link documents, controls, owners, versions, permissions and execution evidence. Software supports proofing but does not replace governance, internal accountability and legal assessments.
What’s the difference between versioning and audit trail? Versioning captures the document evolution and lets you retrieve the version valid for a period. The audit trail logs events such as edits, approvals, permission changes and exports.
Who should be the owner of a compliance document? The owner should normally be the function that governs the related control or process: IT for technical procedures, HR for personnel processes, DPO/privacy owner for privacy documentation, etc., aligned with your organization’s structure.
How should documents from suppliers be handled? Collect supplier documents via controlled channels, record source and date, link them to the relevant control and limit permissions. Clearly separate supplier evidence from internal evidence and record how it was validated.
Do we need to retain every version forever? Not necessarily. Retention depends on legal obligations, risk and internal policy. Practically, avoid deleting versions needed to reconstruct periods already subject to audit, incidents or remediations.
—
AuditReady evidence pack demo — not legal advice