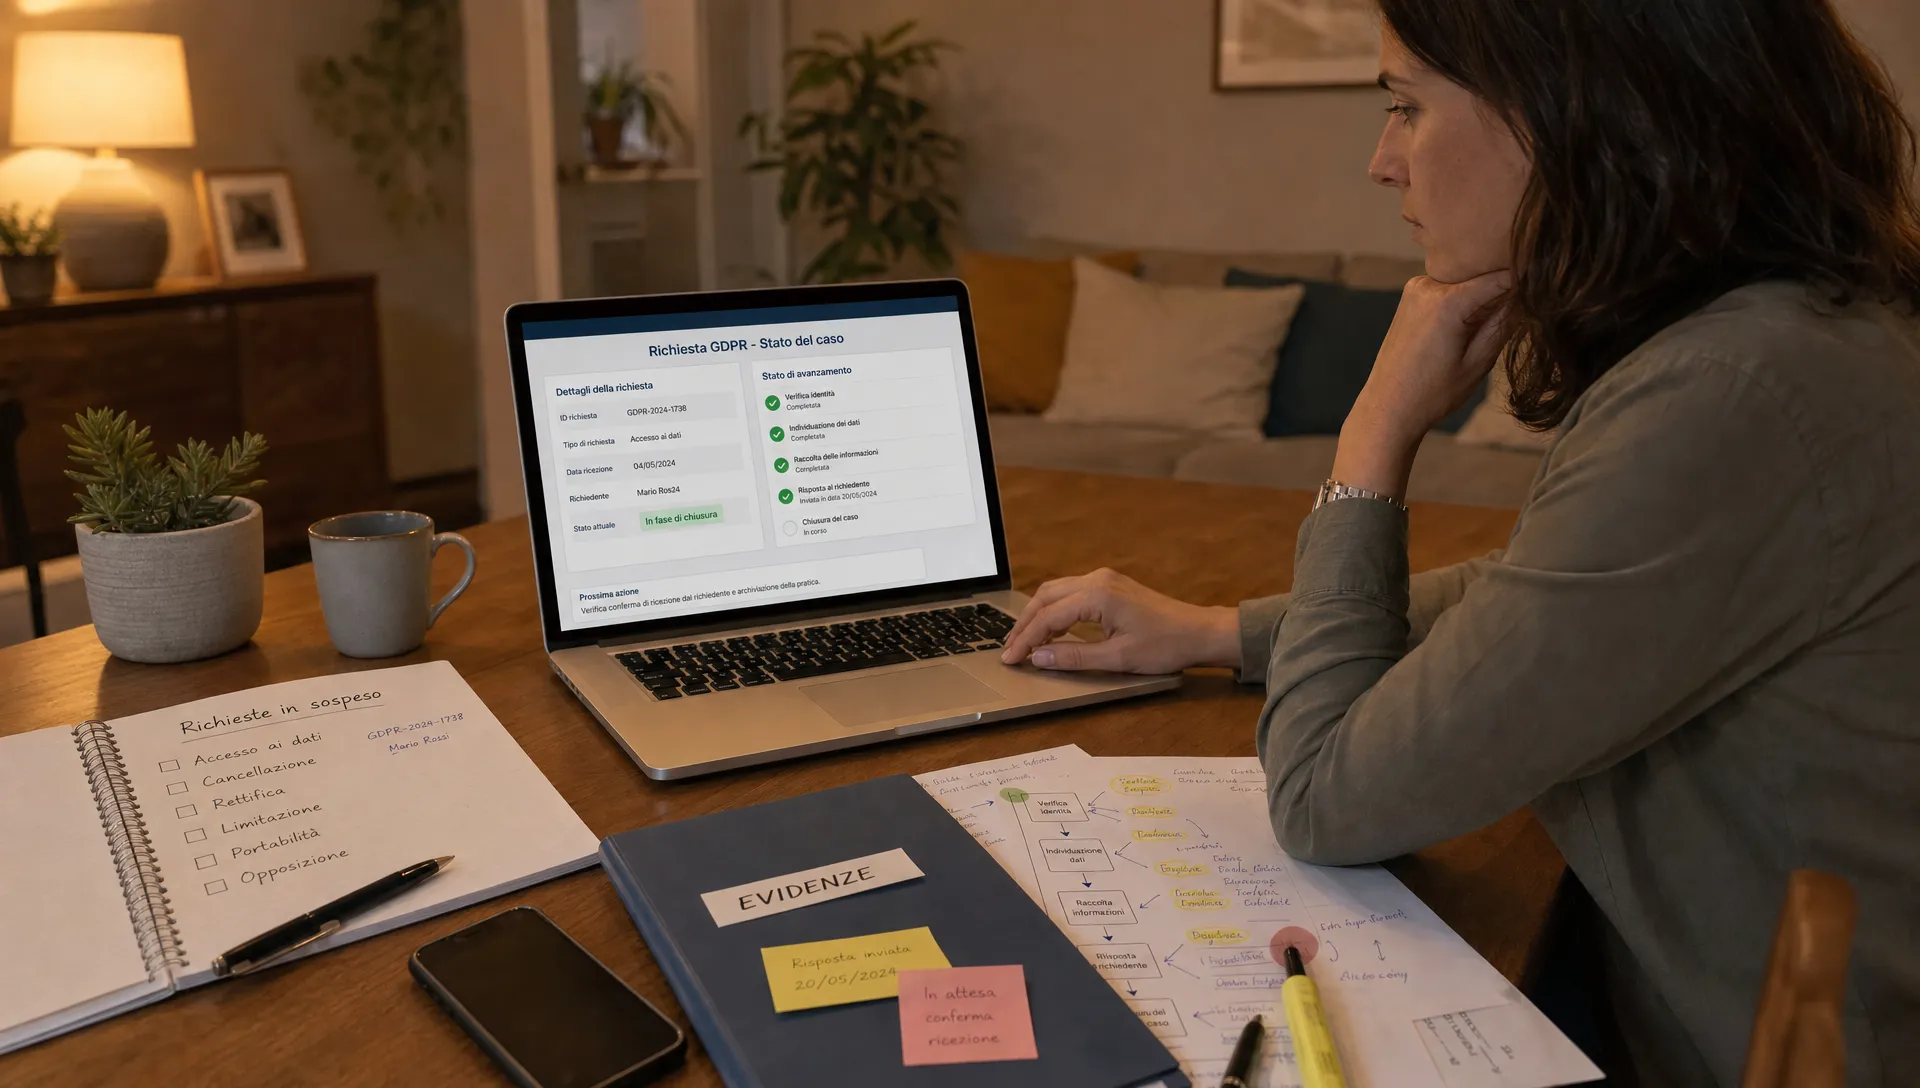
A data subject request isn’t truly closed when a reply is sent; it is closed when you can prove who received it, how it was classified, which systems were checked, what decisions were made and why. Building a GDPR request process that stands up to internal or external review requires moving beyond email folders and ad-hoc tickets toward structured, auditable evidence.
This article gives practical steps for DPOs, compliance managers, CISOs and auditors on how to make requests demonstrably compliant operationally—without replacing legal advice on specific cases.
What “verifiable” means for GDPR requests
Under GDPR, data subject requests cover rights such as access, rectification, erasure, restriction, portability and objection (see Regulation (EU) 2016/679, articles 12+). Operational verifiability asks not only “did we respond?” but “can we independently reconstruct the whole handling of the request?”
A verifiable process links the request record to the treatment mapping, owners, evidence, timelines, responses and closure in a tamper-evident chain. Practically, separate three layers:
- Legal assessment (right exercised, exemptions, legal rationale) — requires privacy/legal expertise.
- Operational workflow (classification, owners, deadlines, actions).
- Evidence package (documents and logs that let an auditor verify what happened).
Map the lifecycle: from intake to closure
Intake and initial classification
Requests arrive through many channels: email, support portals, contact forms, account managers, or in-person. If channels remain siloed, traceability depends on individuals searching mailboxes.
Create a single registration point (a system of record), even when intake stays distributed. Record at minimum: timestamp of receipt, channel, case ID, declared identity, invoked right (or probable right), language, business unit involved and initial priority. The system must prevent requests from staying in a personal inbox without an assigned owner.
Initial classification is routing, not final legal determination. It should trigger owners and start the operational clock for deadlines.
Identity verification, scope and owners
Identity checks should be proportionate to risk. The important evidence is not just the ID copy, but the documented decision: which verification method was used, who approved it, when it completed, and whether any excessive personal data were collected.
Defining the scope (what systems may hold relevant data) is the most common operational gap. CRM, HR, ticketing, marketing automation, billing, document archives and backups all have different owners. Without an up-to-date treatment map, searches become informal and unreliable.
A practical model assigns a case privacy owner who coordinates and technical/business owners who attest which systems they searched. The DPO (if present) provides oversight according to your governance.
Preparing and sending the response
Treat the response as a controlled artifact: versioned text, attached documents or extracts, redactions applied, approvers, the chosen delivery channel and proof of delivery or availability.
GDPR expects responses without undue delay and generally within one month of receipt, with permitted extensions in specific circumstances. Operationally, record any lawful extension decision, with justification and date.
What evidence to keep
Store enough evidence to demonstrate you followed the control objectives, while minimizing unnecessary retention of personal data. Principles: collect what proves the control, protect sensitive content, and set retention aligned with your policies.
Key evidence items:
- Intake: original message, timestamp, channel, case ID — proves when handling began.
- Classification: right requested, case category, priority — shows routing logic.
- Identity: verification method, outcome, approval, date — proves response targeted the right person.
- Data searches: systems consulted, queries or criteria, owners involved — demonstrates the scope of the search.
- Assessment: decision notes, legal limits applied, escalations — provides rationale.
- Response: final text/version, attachments, redactions, approvals — shows what was communicated.
- Delivery & closure: proof of sending or making data available, closure timestamp, final state — closes the loop.
Evidence should be readable to someone who did not handle the case, with metadata connecting items to the control and to owners. For more on audit evidence, see our post on audit trails and logging best practices: /en/blog/audit-trail-best-practices.
Audit trail: what to log and why
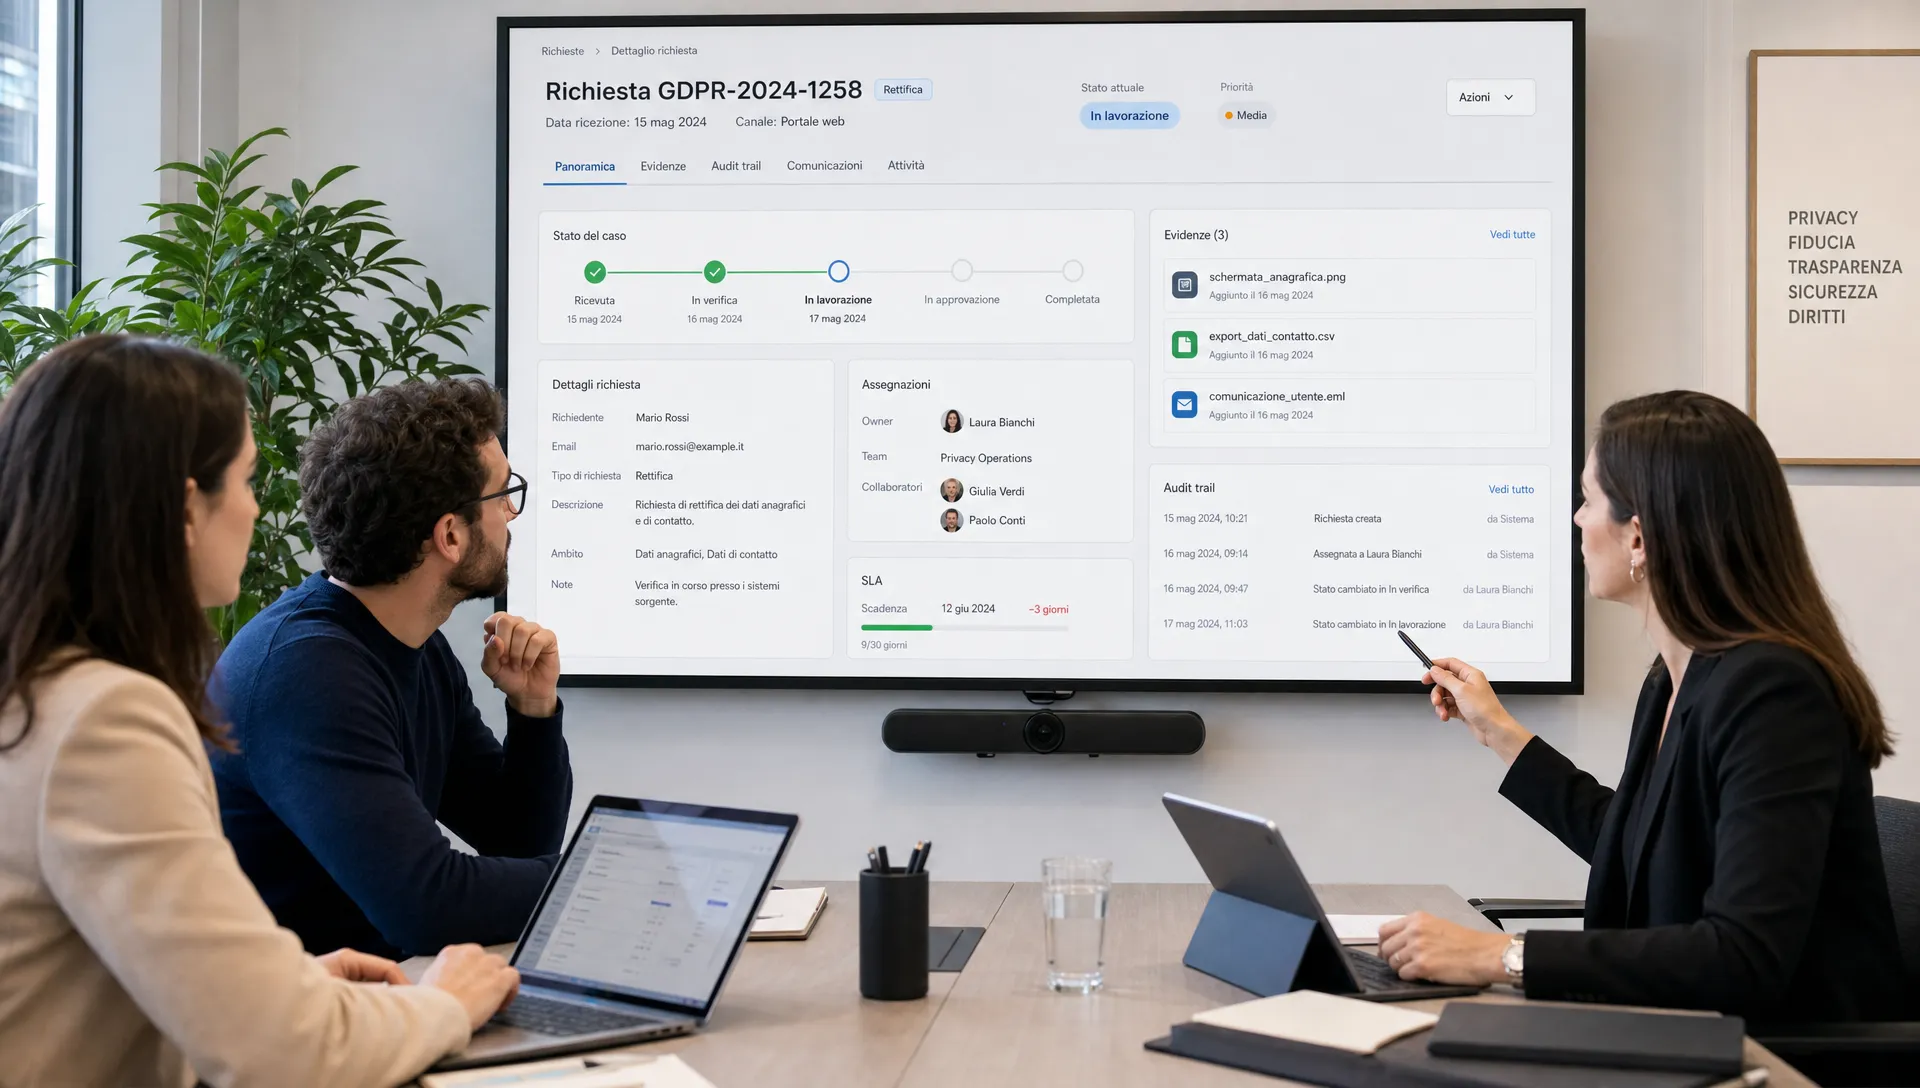
An audit trail for privacy requests must reconstruct critical events: case creation, reclassification, owner assignment, identity verification completion, evidence uploads, approvals, response dispatch and closure. Every event should capture who acted, when and why.
Record version history for key artifacts. If a response is corrected, or the case is reclassified (e.g., from access to erasure), keep previous versions and a note explaining the change. This reduces disputes in audits and helps diagnose process failures.
For more on using logs as evidence, see our guide on building an auditable request workflow: /en/blog/audit-trail-best-practices.
Operational controls to prevent missed SLAs
A verifiable program uses recurring, documented controls, not calendar reminders. Controls must produce evidence of monitoring and remediation.
Suggested controls:
- Open requests queue check (weekly or more often depending on volume): output a list of cases with owners and deadlines; trigger remediation when a case lacks an owner or nears SLA.
- Evidence completeness check (pre-approval): a checklist that certifies required searches and approvals are present; trigger remediation if items are missing.
- Sampling of closed cases (periodic): a review report with outcomes; trigger remediation on repeated errors.
- Channel audits (periodic): verify intake channels are captured by the registration point; trigger remediation if requests are found outside the registry.
- SLA trend review (monthly/quarterly): track delays, root causes and owner responsiveness.
Each finding should generate a remediation action with owner, deadline, corrective steps and proof of completion. The goal is to avoid discovering problems only after a complaint or an audit.
Handling exceptions, complex requests and remediation
Exceptions—generic requests, repeated/overlapping requests, third-party data, employee relations, legacy systems or multi-jurisdictional extractions—are where verifiability often breaks down. Don’t resolve exceptions with undocumented phone calls.
Log the reason for escalation, assign an owner, capture opinions or instructions received, update the case state and link the exception to the final response. If the case reveals a systemic gap (for example, an incomplete treatment map), open a remediation action linking the request to the corrective project.
Linking requests to controls and remediation is what makes your privacy program audit-ready. For a broader compliance model based on controls and evidence, see: /en/blog/gdpr-audit-conformita-dimostrabile.
Common mistakes that break verifiability
- Treating a GDPR request as a generic ticket: tickets often lack structured fields for rights, owners, deadlines and approvals.
- Relying on shared folders with non-standard filenames: a folder full of PDFs doesn’t prove the process—timestamps, authorship, versions and links to controls are usually missing.
- Confusing the response with the evidence: a correct response is weaker in an audit if you can’t show how data were searched, who approved redactions or why a system was excluded.
- Failing to close the improvement loop: solving complex requests ad-hoc without updating maps, playbooks or controls guarantees repeat findings in future audits.
Building an evidence pack for a request
An evidence pack should not be an exhaustive dump. It should enable an auditor to verify the case without reconstructing it from scratch. A practical pack contains:
- Case summary card and timeline.
- Assigned owners and contact points.
- Evidence of searches (system attestations, queries, extracts where appropriate).
- Recorded decisions and approvals (including identity verification method and outcome).
- Final response artifact and proof of delivery.
- Status of any linked remediation actions.
For sensitive requests, separate personal content from the proof of controls: an auditor may not need to read the full personal data extract to verify that the extraction was approved and redactions reviewed.
AuditReady is designed to centralize evidence, controls, risk registers, incidents, privacy logs and audit packs in a single workspace. The operational value is linking every request to owners, versions, an audit trail, remediation and exportable evidence packages—while leaving legal judgment to your privacy or legal function.
FAQs
Q: Is a dedicated mailbox enough to manage GDPR requests? A: A mailbox can be a valid intake channel, but it is not sufficient. You need registration, assigned owners, deadlines, documented searches, approvals and closure proof.
Q: Must I always keep a copy of an identity document? A: There’s no one-size-fits-all operational answer. Define a proportionate verification method, document the outcome and apply data minimization and retention aligned with your privacy policies.
Q: Who should own a data subject request? A: Assign a case privacy owner for coordination plus technical/business owners for each system involved. Involve the DPO according to your governance and their independence requirements.
Q: How detailed should the audit trail be? A: It should let you reconstruct events, actors, dates, versions and the rationale for key decisions. Technical logs without context are weak; freeform notes without versioning are hard to verify.
Want to turn privacy requests into traceable cases with evidence packs ready for review? Learn how AuditReady helps operationalize GDPR requests and build auditable workflows: /en/auditready/lp/gdpr.
Disclaimer: AuditReady provides tooling to centralize evidence and controls; this article is operational guidance and not legal advice.