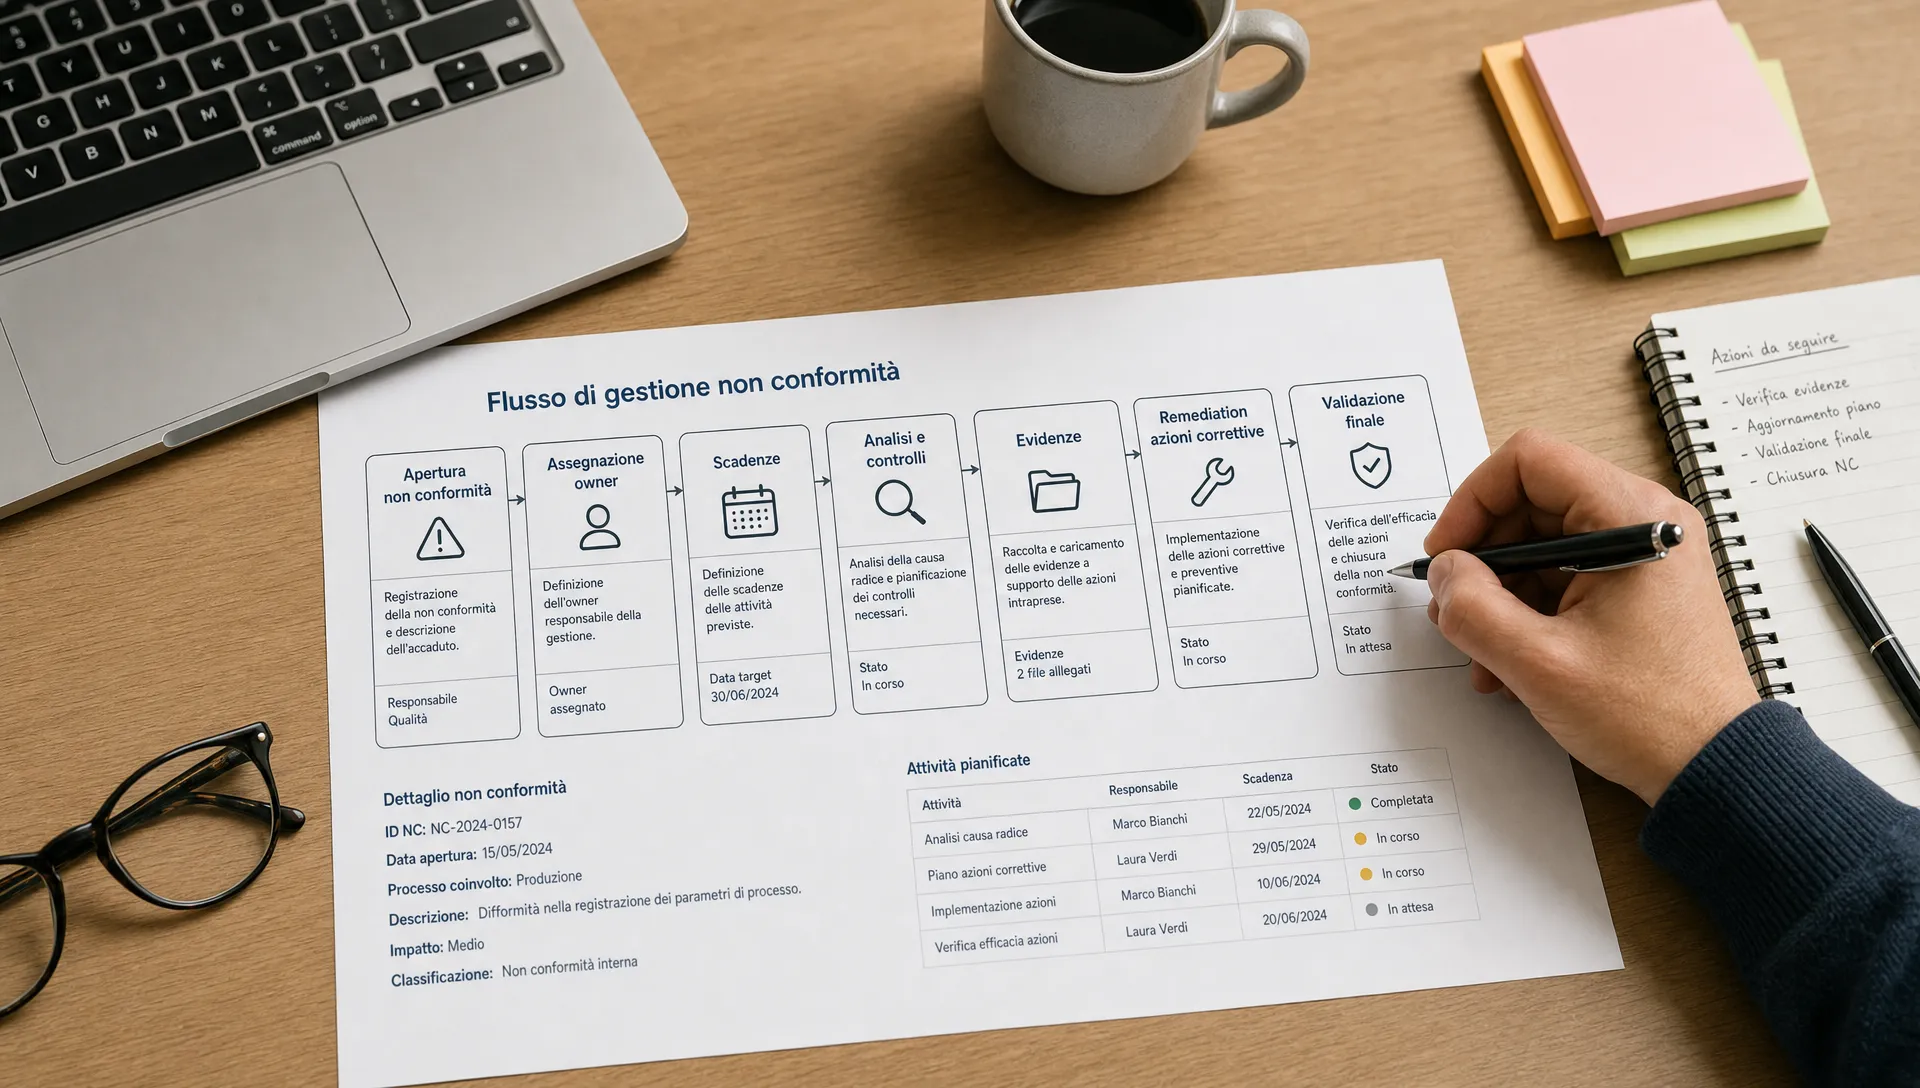
An effective non‑conformity process is not just a list of findings. It’s an operational flow that answers three simple questions for every issue: who owns it, when will it be fixed, and what proof shows it’s fixed? Without a named owner, a realistic deadline and verifiable evidence, even a well‑written finding becomes a loose end during internal reviews, client checks or regulator scrutiny.
This article is practical, not legal. Regulations such as GDPR, NIS2, DORA and ISO standards require documented responsibilities, controls and demonstrable compliance — but here we focus on organizing work, evidence and traceability. For binding legal or regulatory interpretation, consult a qualified advisor.
Why owners and deadlines matter more than long descriptions
A clear description of a non‑conformity is necessary, but insufficient. Auditors and regulators aren’t only looking for a catalogue of issues: they want proof that your organization detects, assigns, remediates, verifies and prevents recurrence. That proof is demonstrated by a chain of accountability: requirement → failed control or event → named owner → corrective action → evidence → validation.
Treat non‑conformities as a workflow of responsibility, not a filing cabinet of problems.
Minimal operational workflow: what every finding should include
Keep the workflow simple enough for regular use but robust enough to survive scrutiny. If the process is too cumbersome, teams will revert to emails and spreadsheets — and you’ll lose auditability.
Opening a finding: record a verifiable fact
Start from an observable fact: “Quarterly review of admin access not documented for Q2” is far more actionable than “weak access controls.” At a minimum, every new finding should include:
- source of the finding (audit, control test, incident, third‑party request)
- relevant requirement or control (GDPR article, NIS2 requirement, ISO control number)
- impact or potential consequence
- date detected and reporter
If you’re building a register from scratch, begin with a basic fields template and layer governance for closure separately. See our guide on structuring an issues register: /en/blog/come-strutturare-il-registro-delle-non-conformita-e-le-azioni
Assignment: an accountable person, not a department
Assign an owner who can coordinate the remediation. Avoid ambiguous assignments such as “IT” or “Legal.” Useful role distinctions:
- Owner: coordinates the fix and owns updates
- Contributors: perform specific tasks (configuration, patching, paperwork)
- Approver/Validator: independently confirms the remediation is effective
For findings involving vendors, keep an internal owner who manages the supplier interaction and documents requests, responses and acceptance criteria.
Deadlines: align them with risk and feasibility
Deadlines should reflect impact, urgency, technical dependencies and resource availability. To avoid arbitrary dates, define a few priority classes (e.g., Critical, High, Medium, Low) with clear escalation rules. Example operational criteria:
- Critical: immediate security or regulatory impact — escalate to senior management, require independent validation
- High: control not performed or evidence missing for a key requirement — require owner validation and test evidence
- Medium: contained deviation with manageable impact — corrective action and artifacts
- Low: documentation or process alignment — document update and communications
Link deadlines to priority and require documented rationale for any extension.
Connecting findings, controls, risks and evidence
The common weakness is not the existence of a register but the lack of linkage between a finding and the underlying control, test or risk. A finding that doesn’t reference the failed control and the missing evidence becomes self‑referential.
A demonstrable process keeps a readable chain: requirement → control → triggering test/event → owner → remediation tasks → evidence → final validation. That chain answers the auditor’s core question: “Why do you consider this closed?”
What counts as closure evidence
Evidence must be proportional and relevant to the root cause. Examples:
- Missing access reviews: review report, revocation list, owner approval and timestamped logs
- Missing procedure: approved document, circulation record, and evidence of first execution
Avoid weak evidence like isolated screenshots or uncontextualized emails. Good evidence enables an independent reviewer to understand what was done, when, by whom and with what result.
Audit trail: what must remain visible
An audit trail is more than change history. It must reconstruct decisions. When a deadline is extended, record who changed it, when, why and who approved the extension. When a finding is reclassified, link the justification to the risk assessment.
Minimum traceability items: state changes, owner changes, deadline extensions, attachments, relevant comments, approvals and final closure metadata. Consider established best practices for audit trails: /en/blog/audit-trail-best-practices
Remediation: from a promise to proven effectiveness
A finding isn’t closed when an owner says “done.” It’s closed when evidence proves the corrective action reduced the deviation or risk to an acceptable level and an independent validation has taken place where appropriate.
Verification may be performed by a control owner, internal audit, DPO, CISO or another independent role, depending on severity. Verification should answer three questions:
- Was the promised action completed?
- Does the evidence demonstrate the correction?
- Should the control be updated to prevent recurrence?
If any answer is uncertain, don’t close the finding.
When extensions are acceptable
Extensions are valid when documented: cause, new date, impact on risk, temporary compensating controls and an approver. They’re problematic when frequent, unapproved or approved by the same person who missed the original date. Governance issues should be escalated.
Operational dashboard: fewer, actionable indicators
A dashboard should reveal where to act, not just how many findings exist. Useful metrics:
- open findings by priority
- overdue findings by owner
- average time to close by category
- number of extensions
- recurrent findings on the same control
- items pending validation
Metrics must drive decisions: reallocate resources, escalate to management, update controls, open new risks or request supplier evidence.
Common mistakes to avoid
- Closing on plans rather than evidence. A plan is a commitment; evidence shows execution.
- Assigning owners at the wrong level. Sponsors vs. operational owners must be distinct.
- Treating remediation separately from risk management. Structural weaknesses require updates to risk assessments and recurring tests.
- Storing evidence outside the workflow in personal folders or email threads. During an audit, it’s not enough to find a file — you must show it’s the approved version linked to the closure.
Quick FAQ
Who should be the owner? The person or role who can coordinate the remediation and is accountable for operational closure — not necessarily the person who performs every task.
Can a finding be closed without evidence? Not in an audit‑ready process. Closure must be supported by verifiable artifacts: approved documents, logs, reports, tickets, or tests.
How to handle overdue deadlines? Overdue items require escalation, an updated risk assessment and documented rationale. Extensions must include cause, new date, compensating controls and approval.
Corrective vs preventive actions: corrective actions fix the detected issue; preventive actions reduce the chance of recurrence (e.g., updating a control, adding periodic tests or clarifying responsibilities).
Bring owners, deadlines and evidence into one flow
If you’re centralizing remediation and evidence for privacy or regulatory audits, consider AuditReady for GDPR and broader compliance workflows: /en/auditready/lp/gdpr. AuditReady helps connect findings, owners, deadlines and verifiable evidence in a single operational flow.
AuditReady evidence pack demo / not legal advice