
Privacy Notice Obligations and Evidence Tracking in AuditReady
This guide explains how AuditReady manages obligations related to GDPR Articles 13 and 14 privacy notices, showing the link between the regulatory requirement, assigned responsibilities, supplier requests, received confirmations, uploaded documents, and the control’s coverage status.
Step 1: Understand the privacy notice obligation
The obligation concerns the privacy notices required by Articles 13 and 14 of the GDPR. The organization must be able to demonstrate:
- which personal data is processed,
- for what purposes,
- the legal basis for processing,
- retention periods,
- the rights data subjects can exercise.
These details need to be clearly tracked and verifiable within AuditReady.
Step 2: Locate the requirement in the annual GDPR compliance review
In AuditReady, the privacy notice requirement is included in the GDPR 2026 annual compliance review. Opening this review shows that specific responsibilities are assigned to the requirement:
- Alessandra
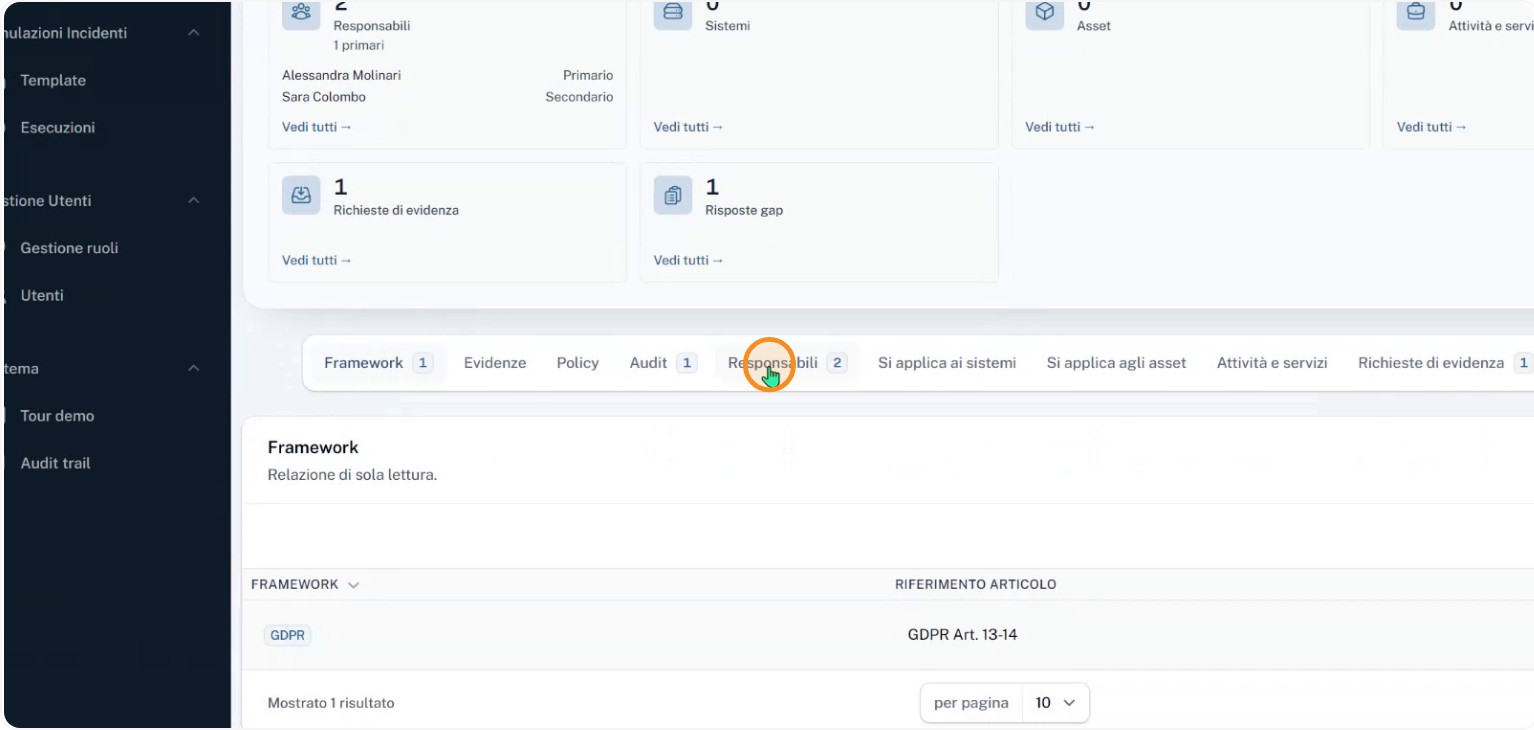
Molinari as the primary contact,
- Sara Colombo as the secondary responsible.
Confirm that these roles are correctly configured and up to date.
Step 3: Check the evidences linked to the supplier request
Within the same control you can also view the result of the request previously sent to Norming Logistica in the demo.
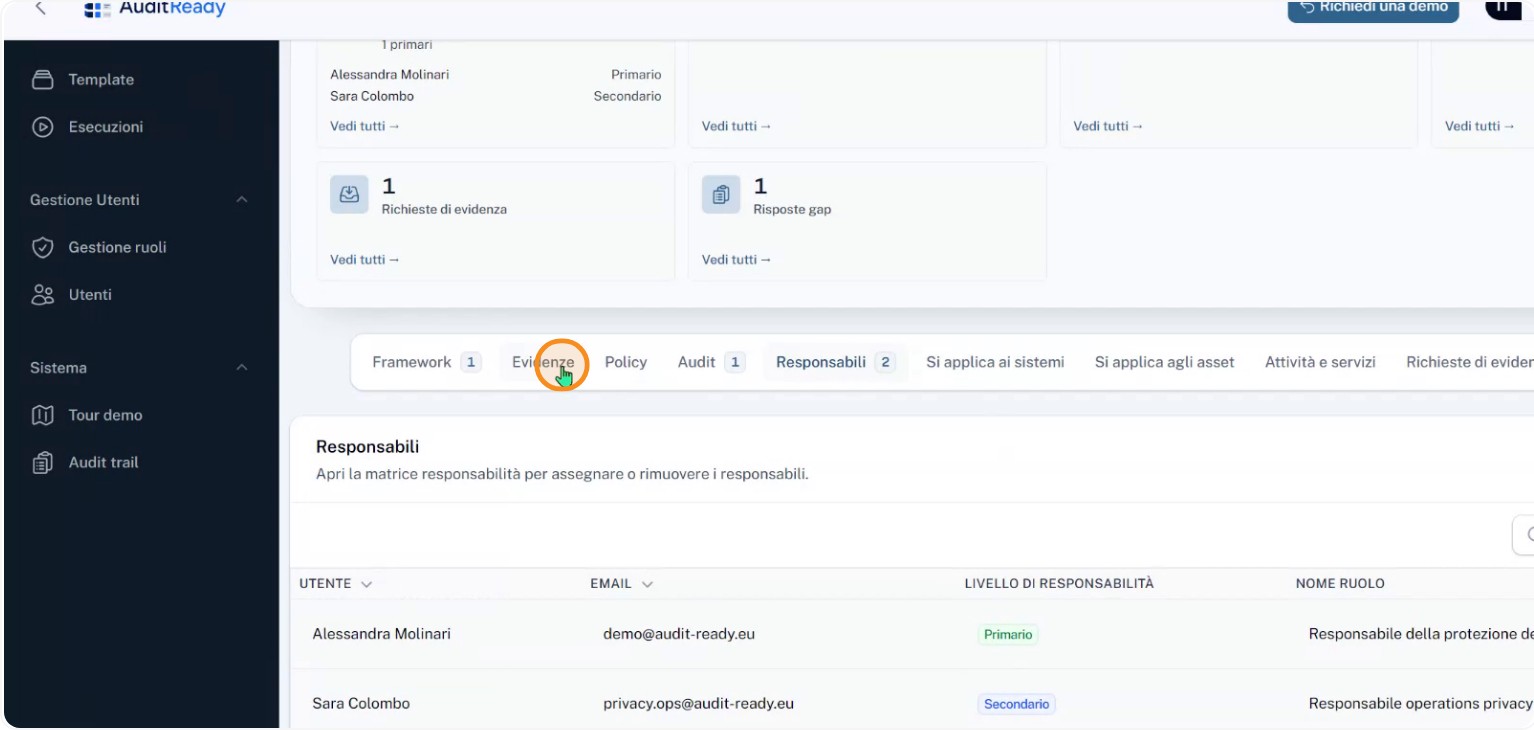
This section shows that the following items have been collected and linked:
- the confirmation of having viewed the notice,
- the notice that was viewed,
- the uploaded document.
Ensure all of these elements are present and correctly associated with the request sent.
Step 4: Verify the connections between documents, recipient and audit
The evidences are not three isolated files: they remain connected to:
- the recipient,
- the original request,
- the snapshot of the confirmation moment,
- the audit where they will be used.
Open each evidence to confirm you can always trace back to the full context (request, recipient, confirmation and related audit).
Step 5: Review the control status and missing coverage
A status of "to be reviewed" means the control’s coverage is not yet complete.
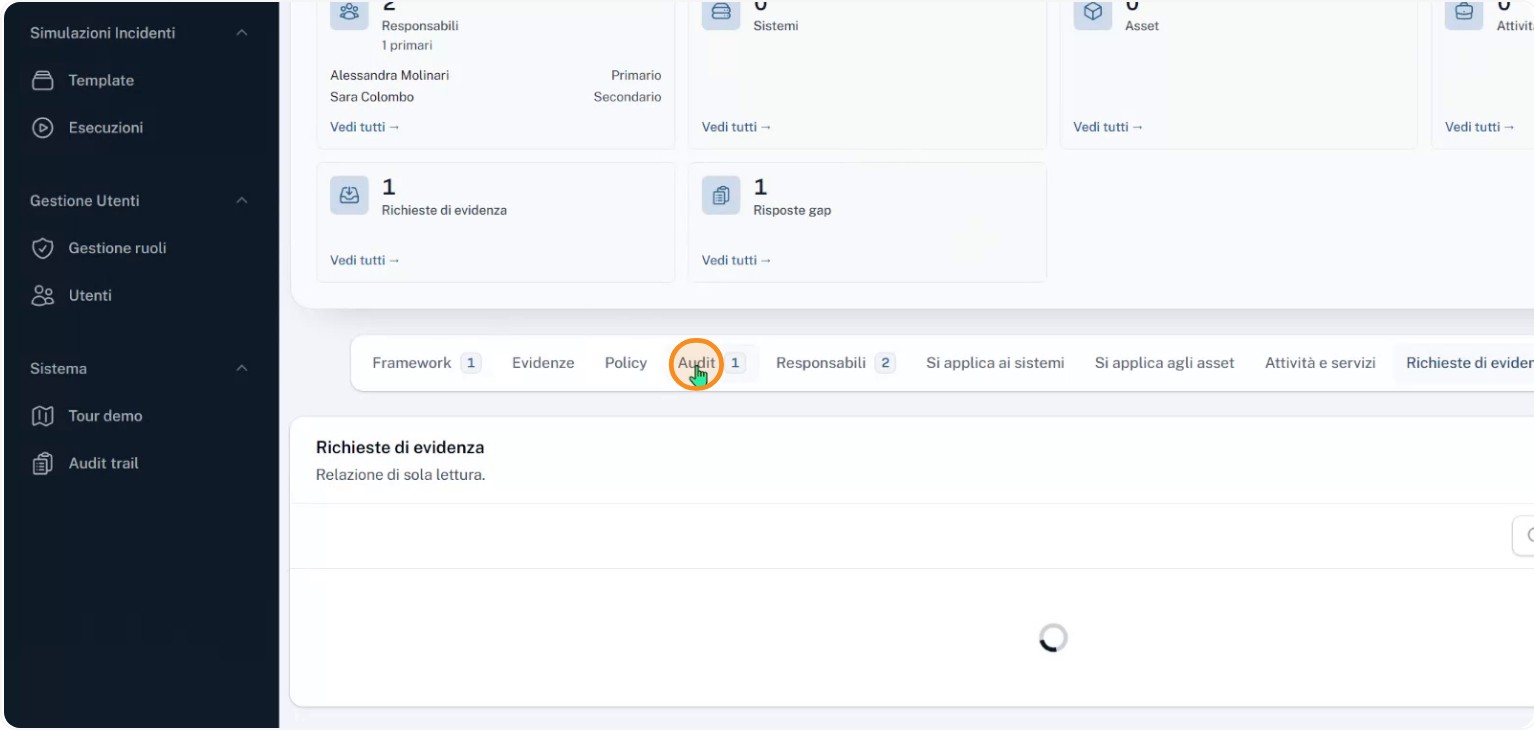
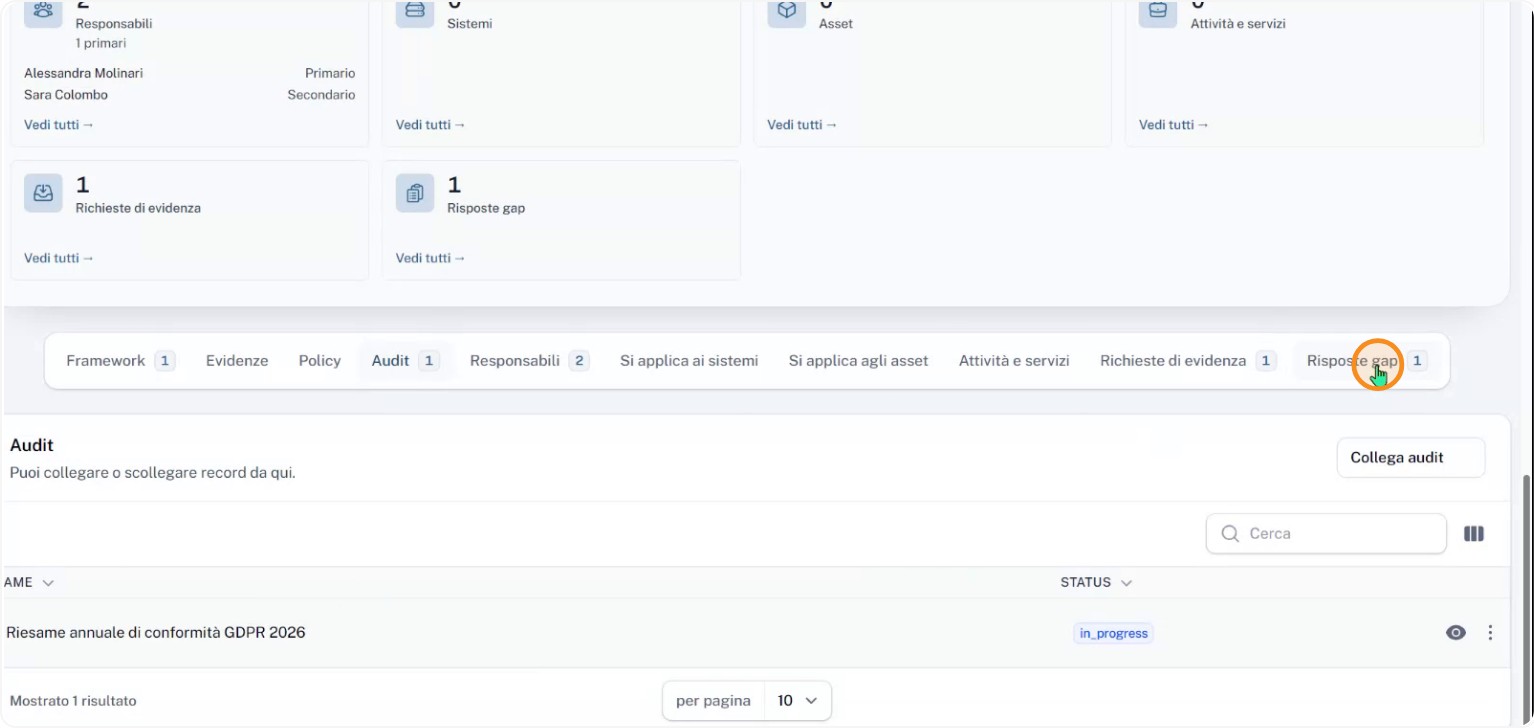
For example, the control may still lack an associated policy.
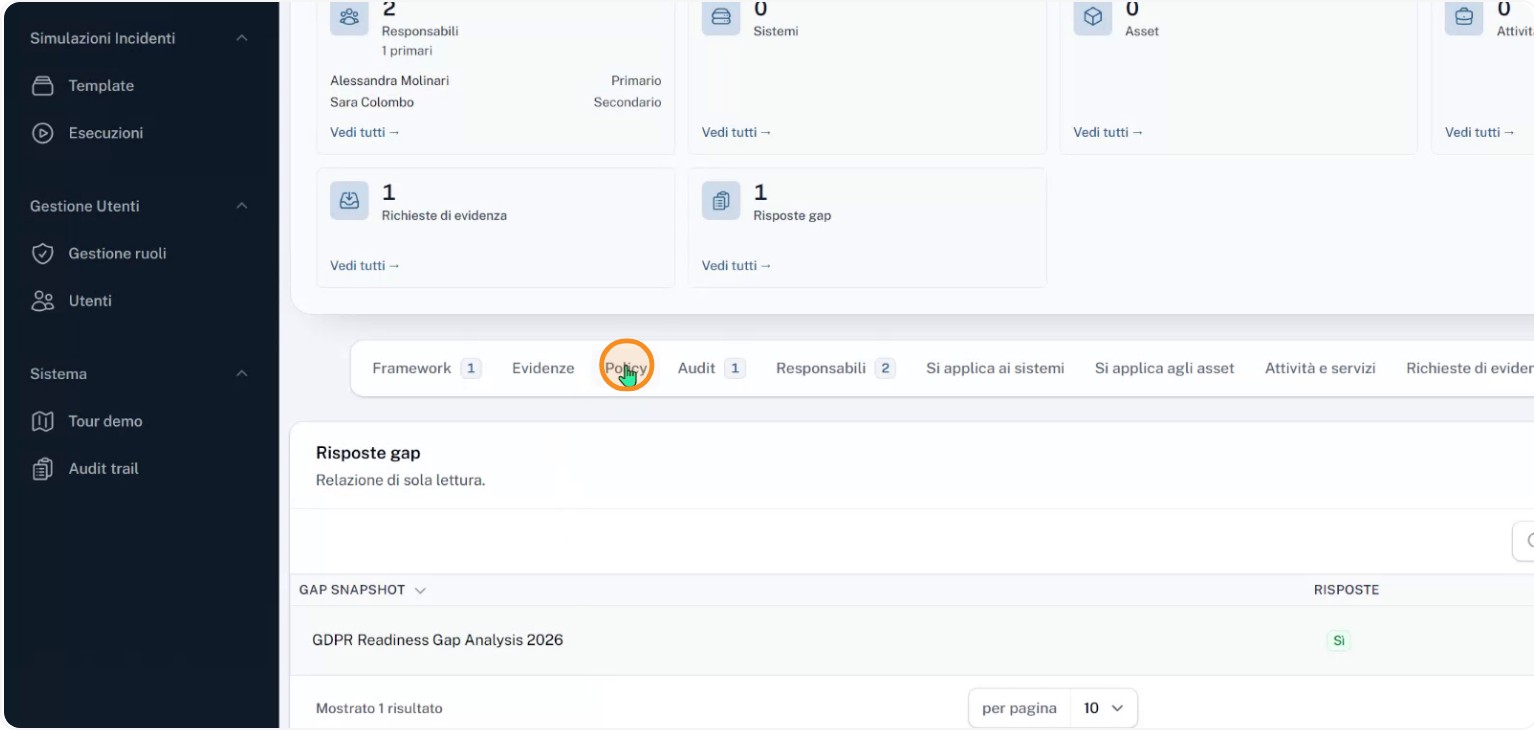
You should:
- identify which elements are missing (e.g., policy not linked),
- plan and record the actions needed to complete the coverage.
This way AuditReady makes the entire journey visible: from the regulatory obligation to assigned responsibility, through collected evidence and items still outstanding.