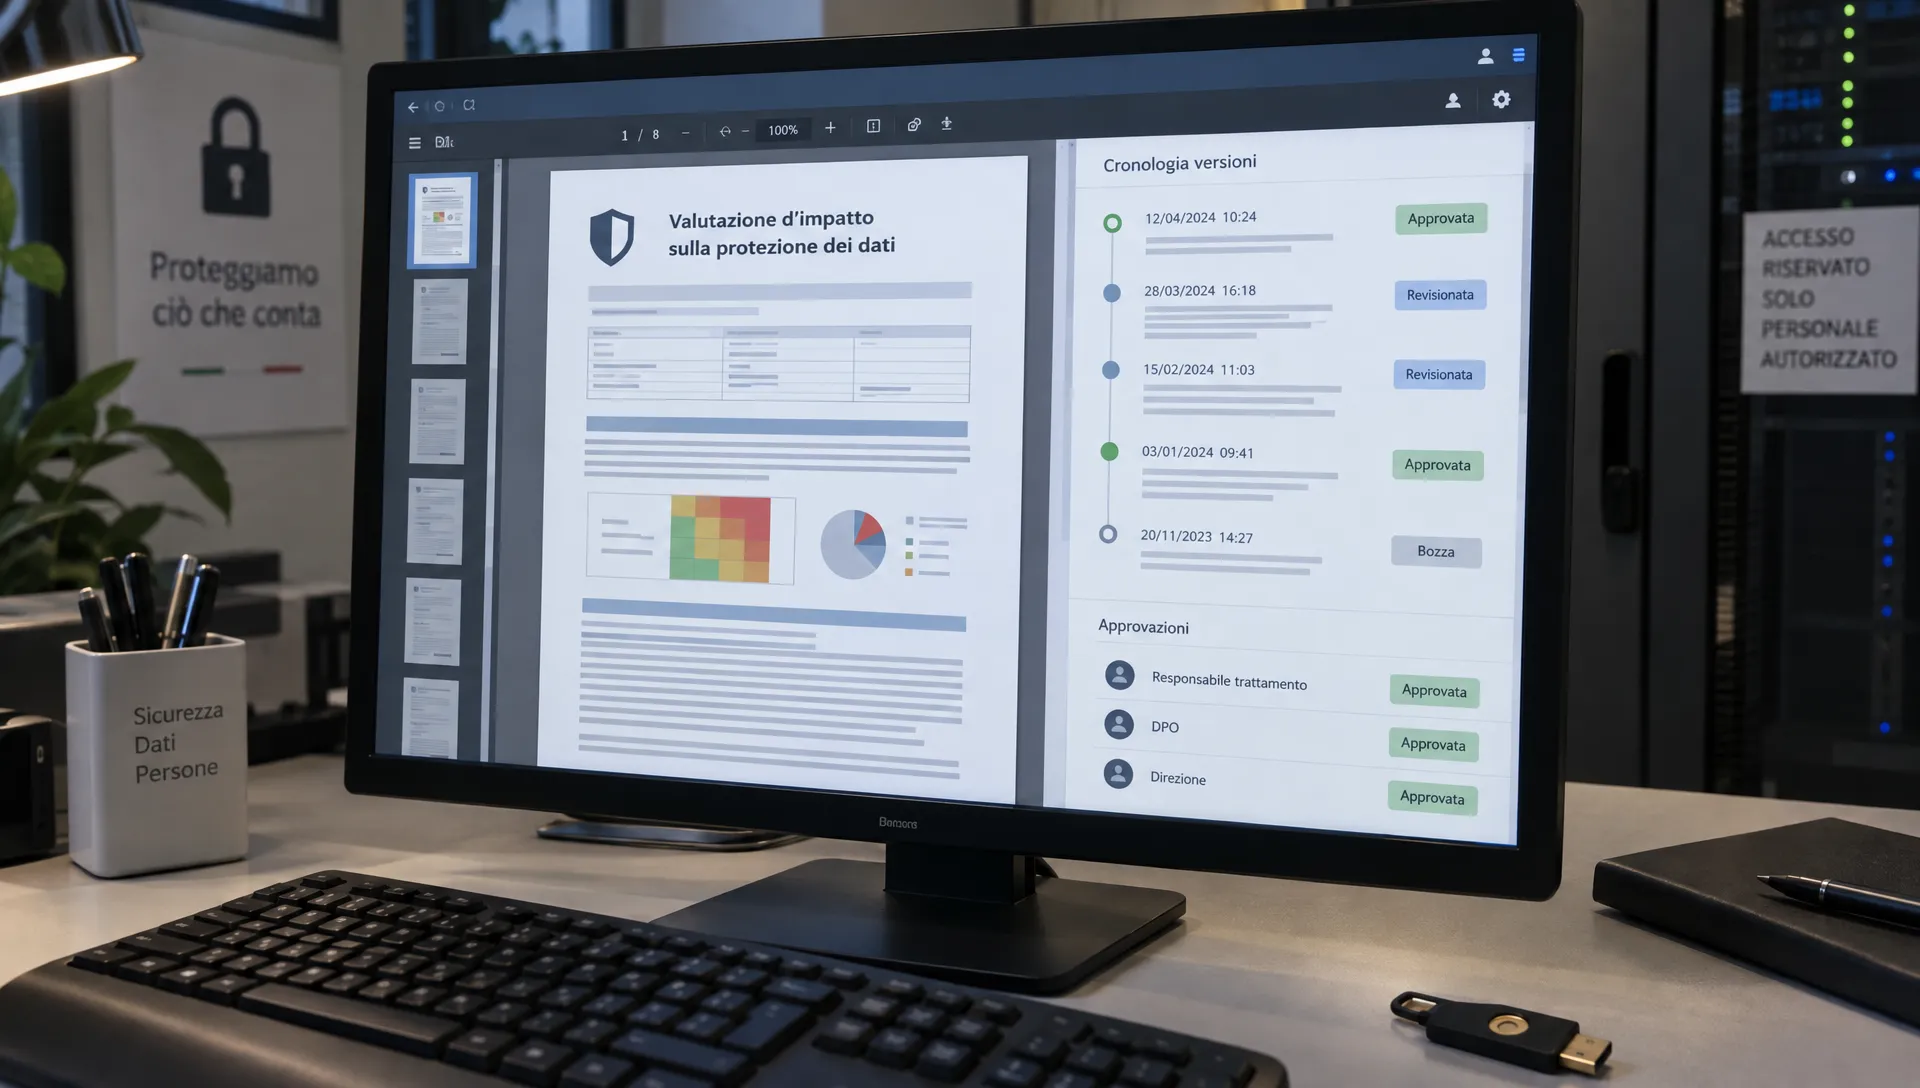
How to evaluate a DPIA software by testing role separation, audit logs, and approval traceability. Practical demo checklist and guidance for procurement decisions.
dpia software
Aggiornamenti su AuditReady, evidence operations e audit readiness.
How to evaluate a DPIA software by testing role separation, audit logs, and approval traceability. Practical demo checklist and guidance for procurement decisions.
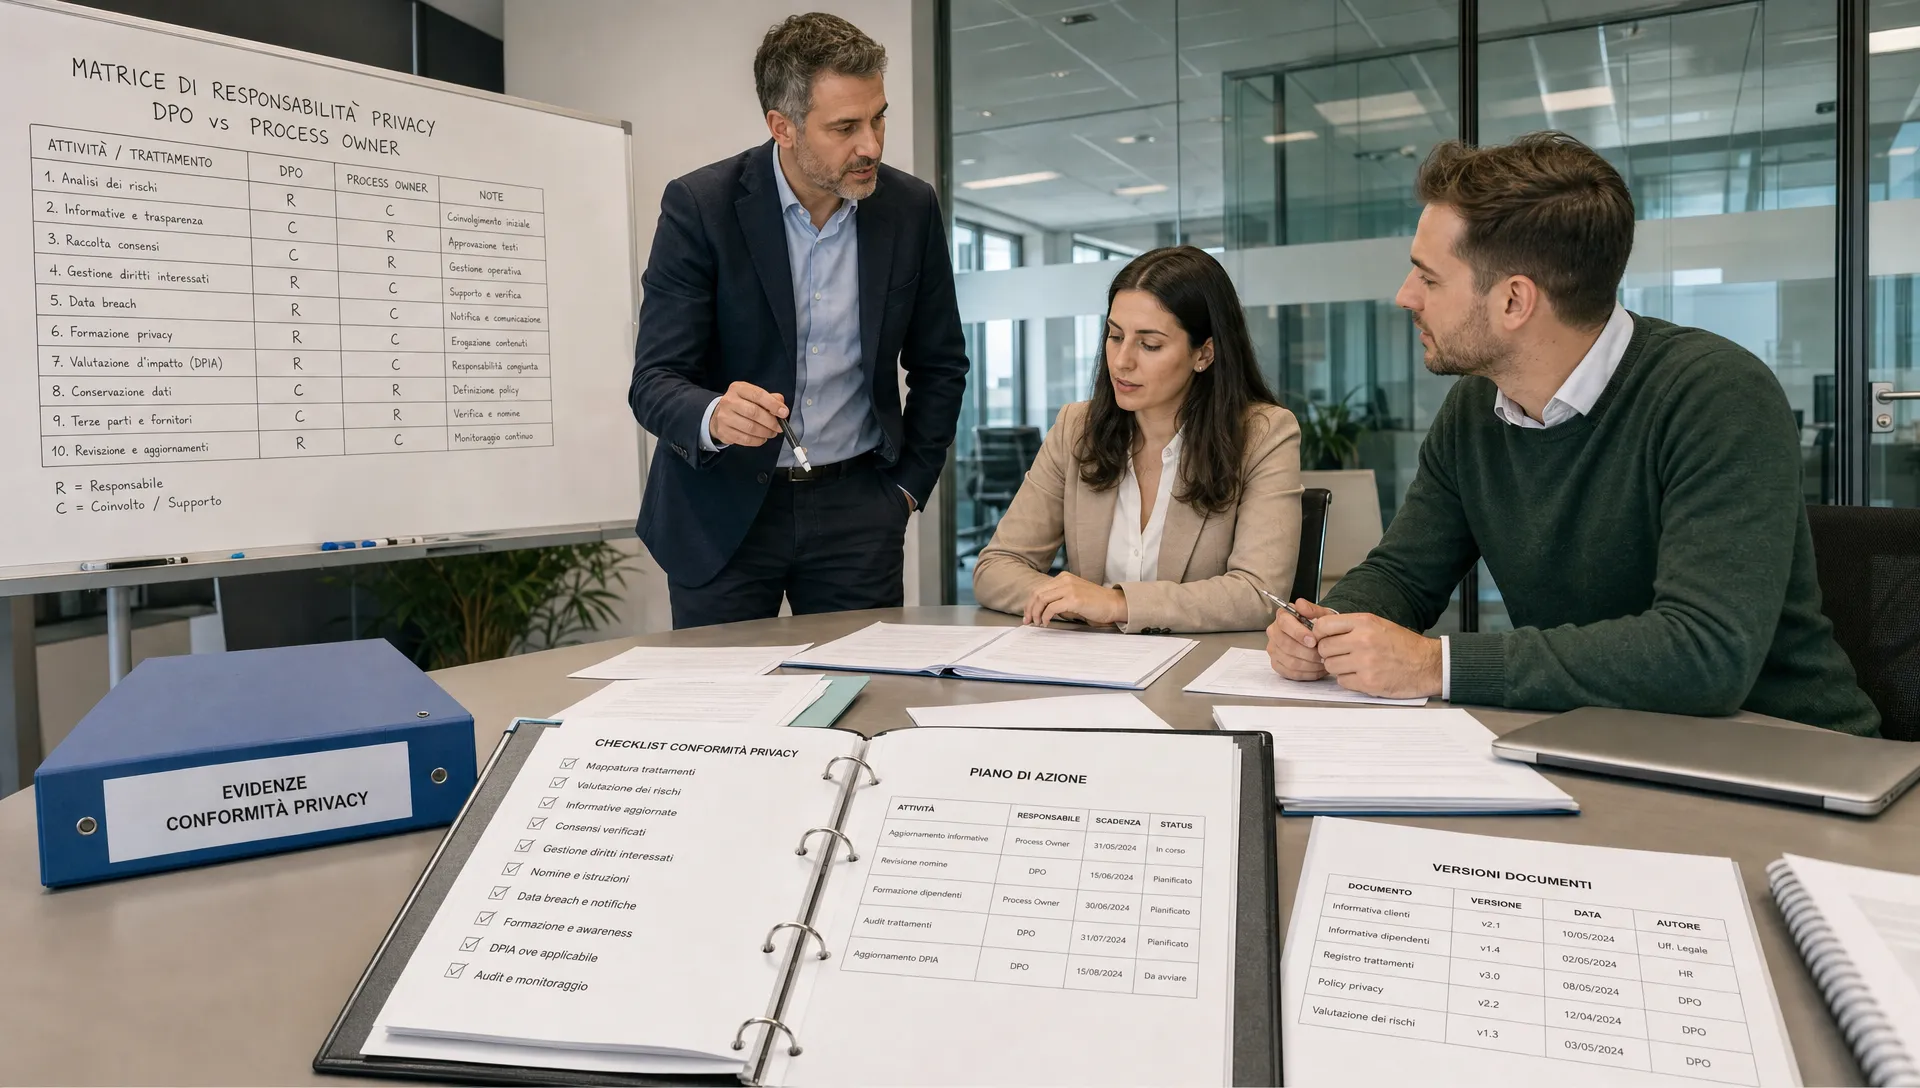
Create a verifiable privacy governance model that assigns decisions, controls, evidence, audit trails and remediation between the DPO, process owners and operational teams.
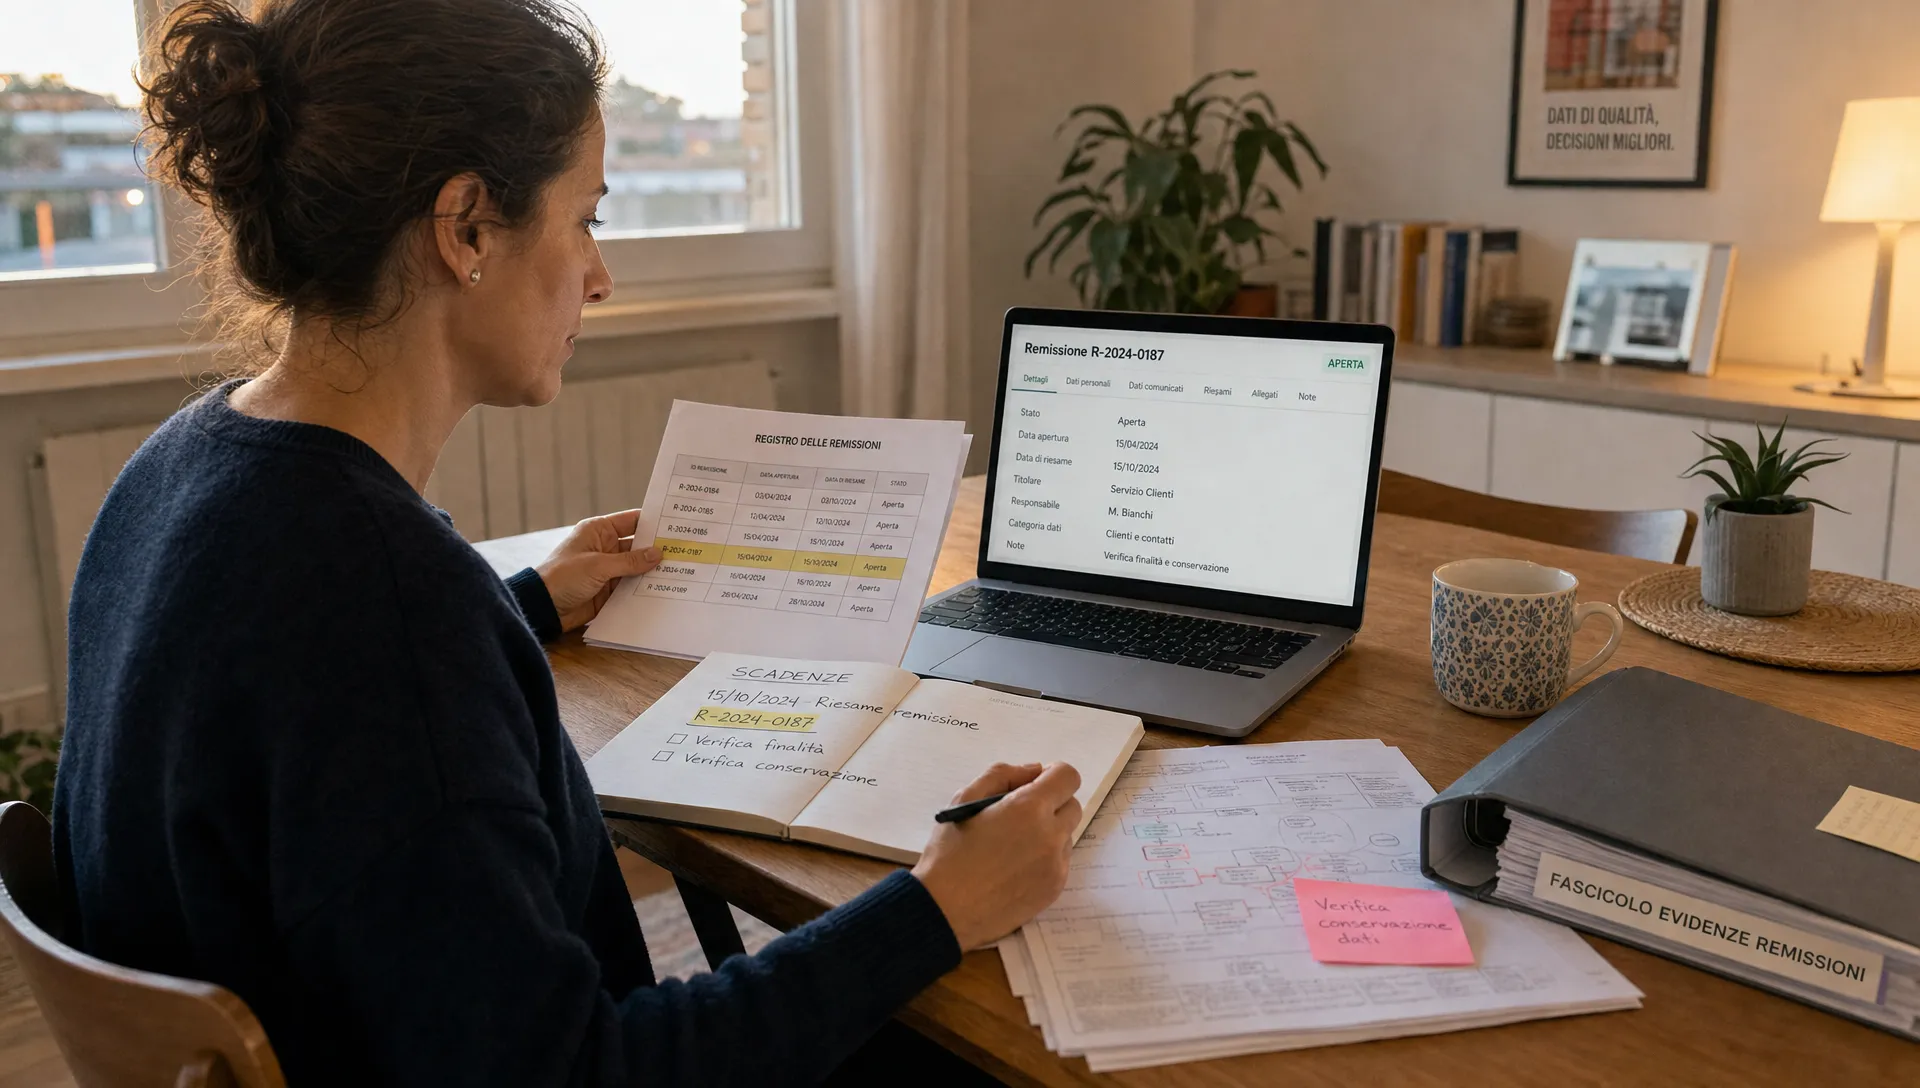
How to record decisions, exceptions, owners, evidence and remediation so your data governance is auditable against GDPR, NIS2, DORA and other frameworks.
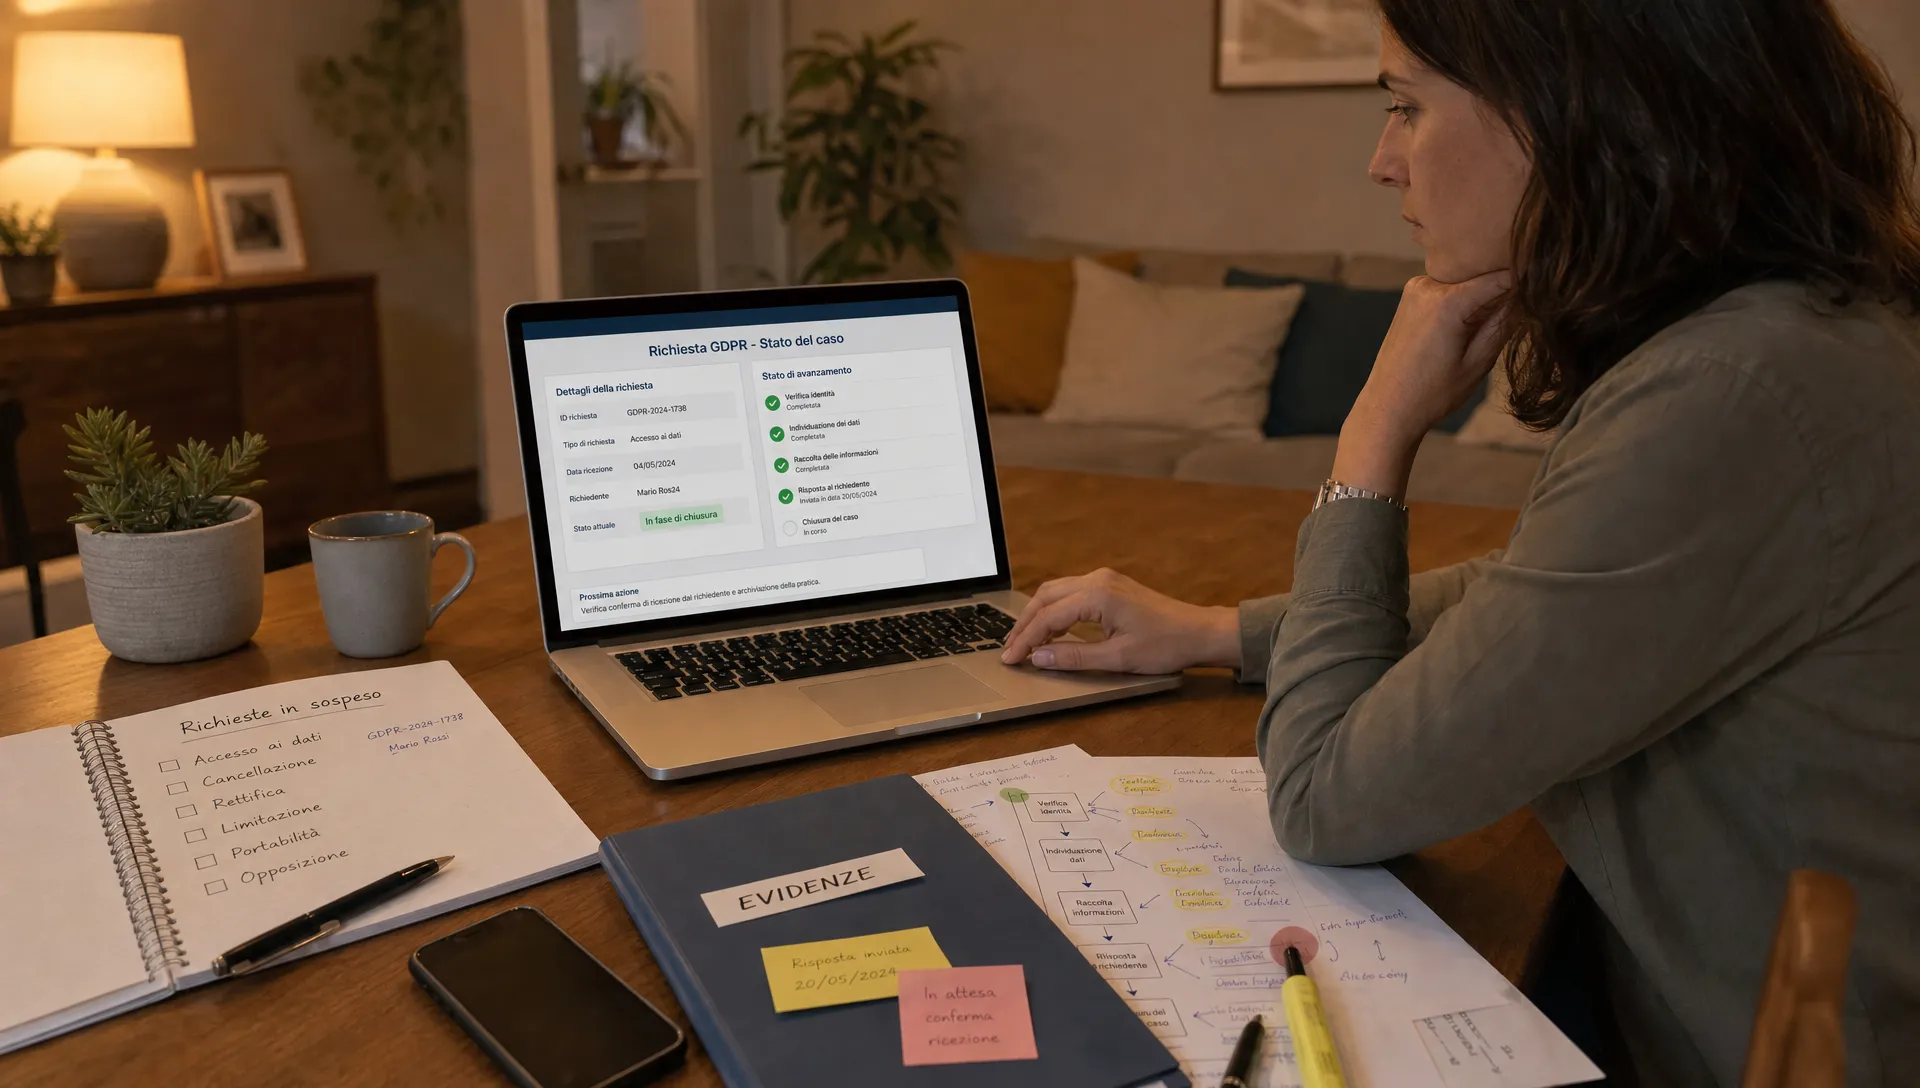
How to design an operational GDPR request process that produces verifiable evidence: intake, identity checks, system searches, owners, audit trail, remediation and evidence packs.
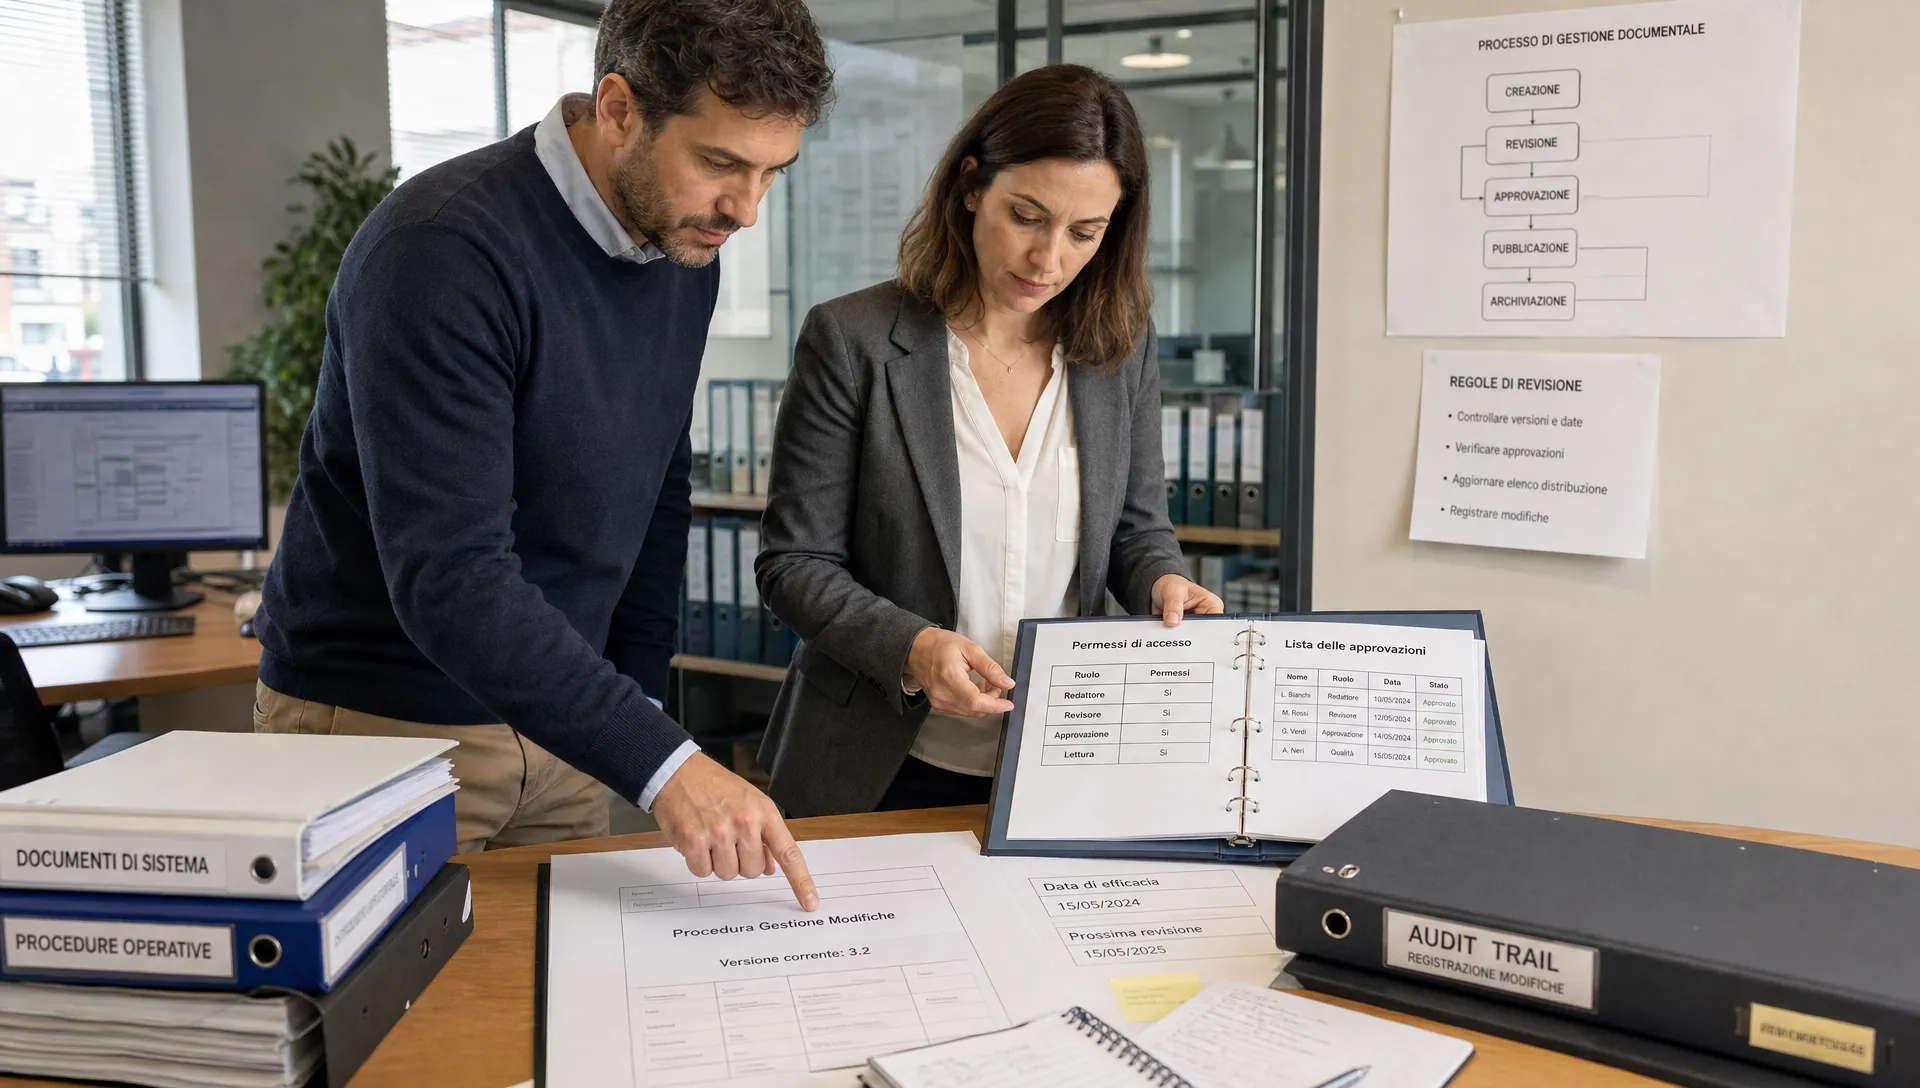
Turn your document repository into an auditable system: manage versions, assign owners, control permissions and keep an accessible audit trail to produce verifiable evidence without chaos.
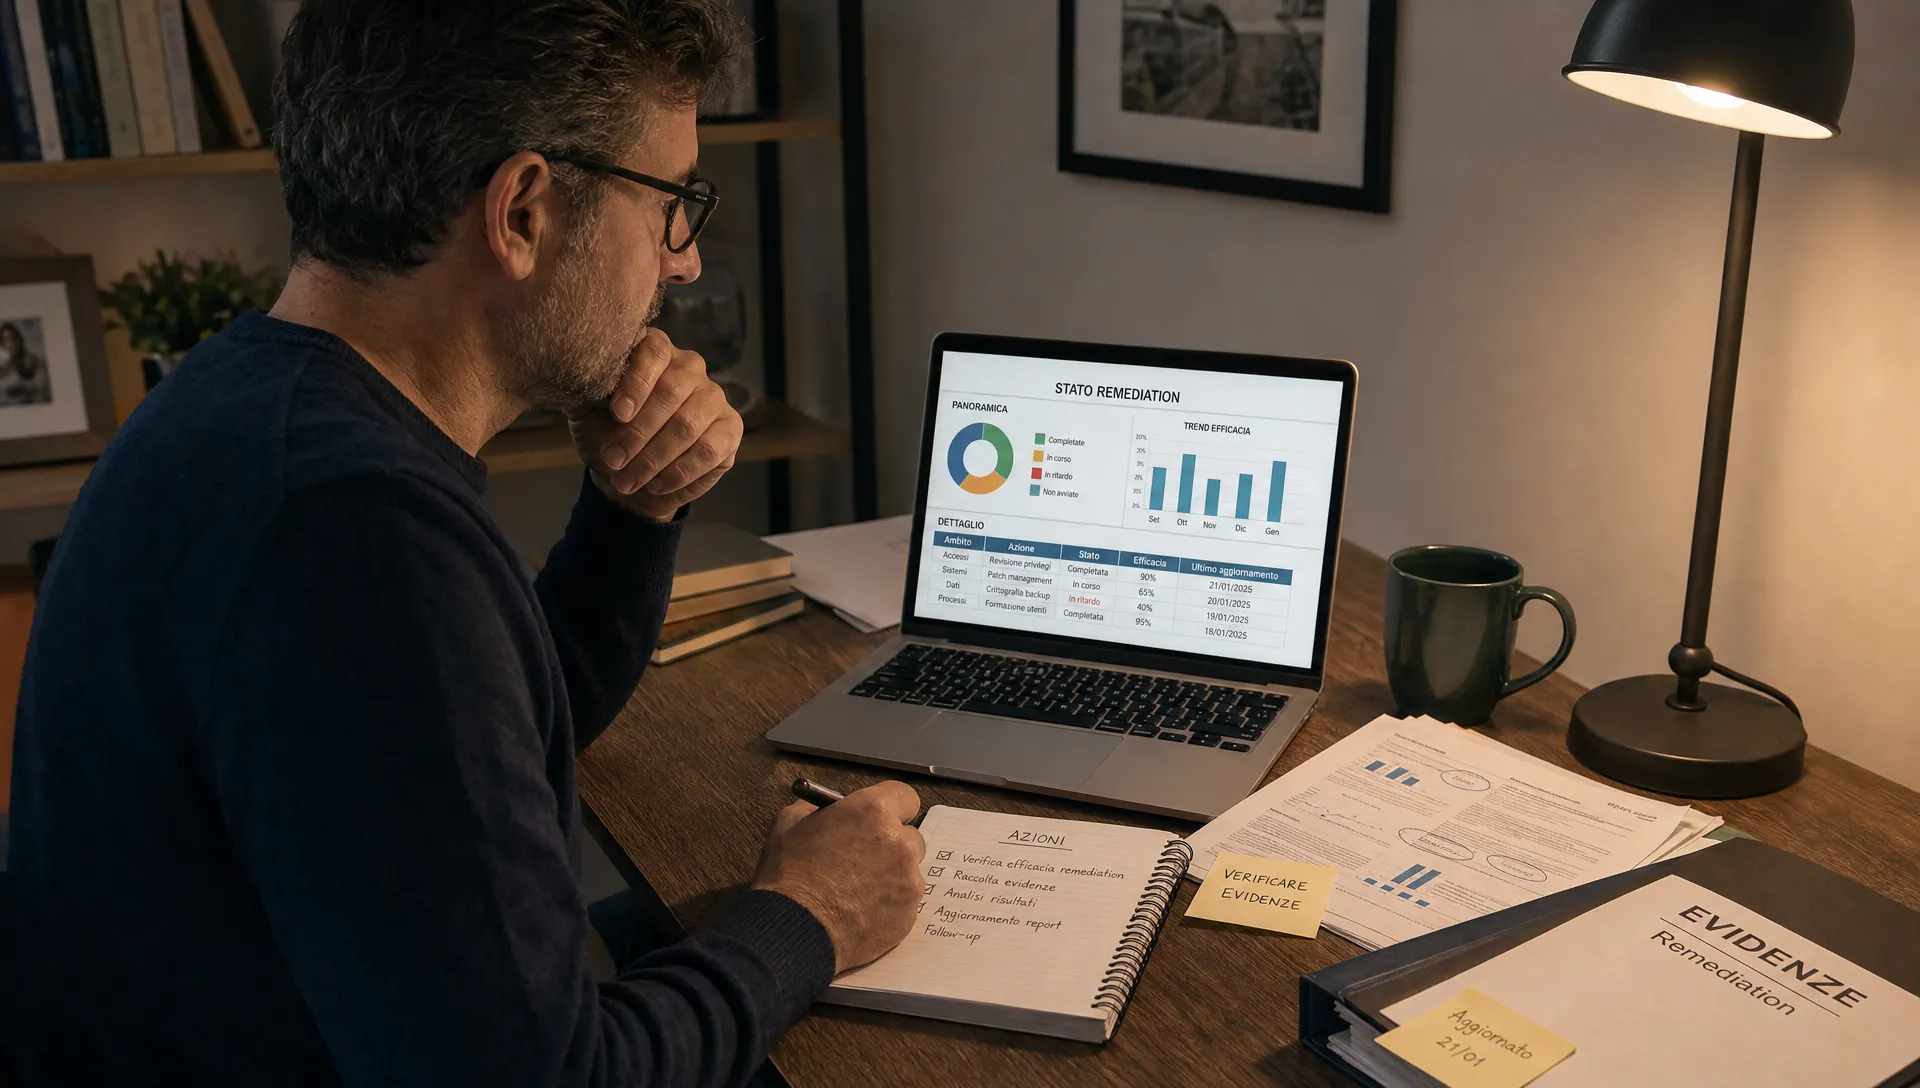
Learn practical steps to prove remediation works: define acceptance criteria, collect reusable evidence, retest controls, and keep an audit-ready trail for GDPR, NIS2, DORA and other frameworks.
Could not load more posts. Try again or open the next page from the address bar.